GateKeeper
One sign-in for everything you self-host
An authentication server in a single container. Protect any app with OIDC or your reverse proxy, and sign in with passkeys, an authenticator, an emailed code, or your phone.
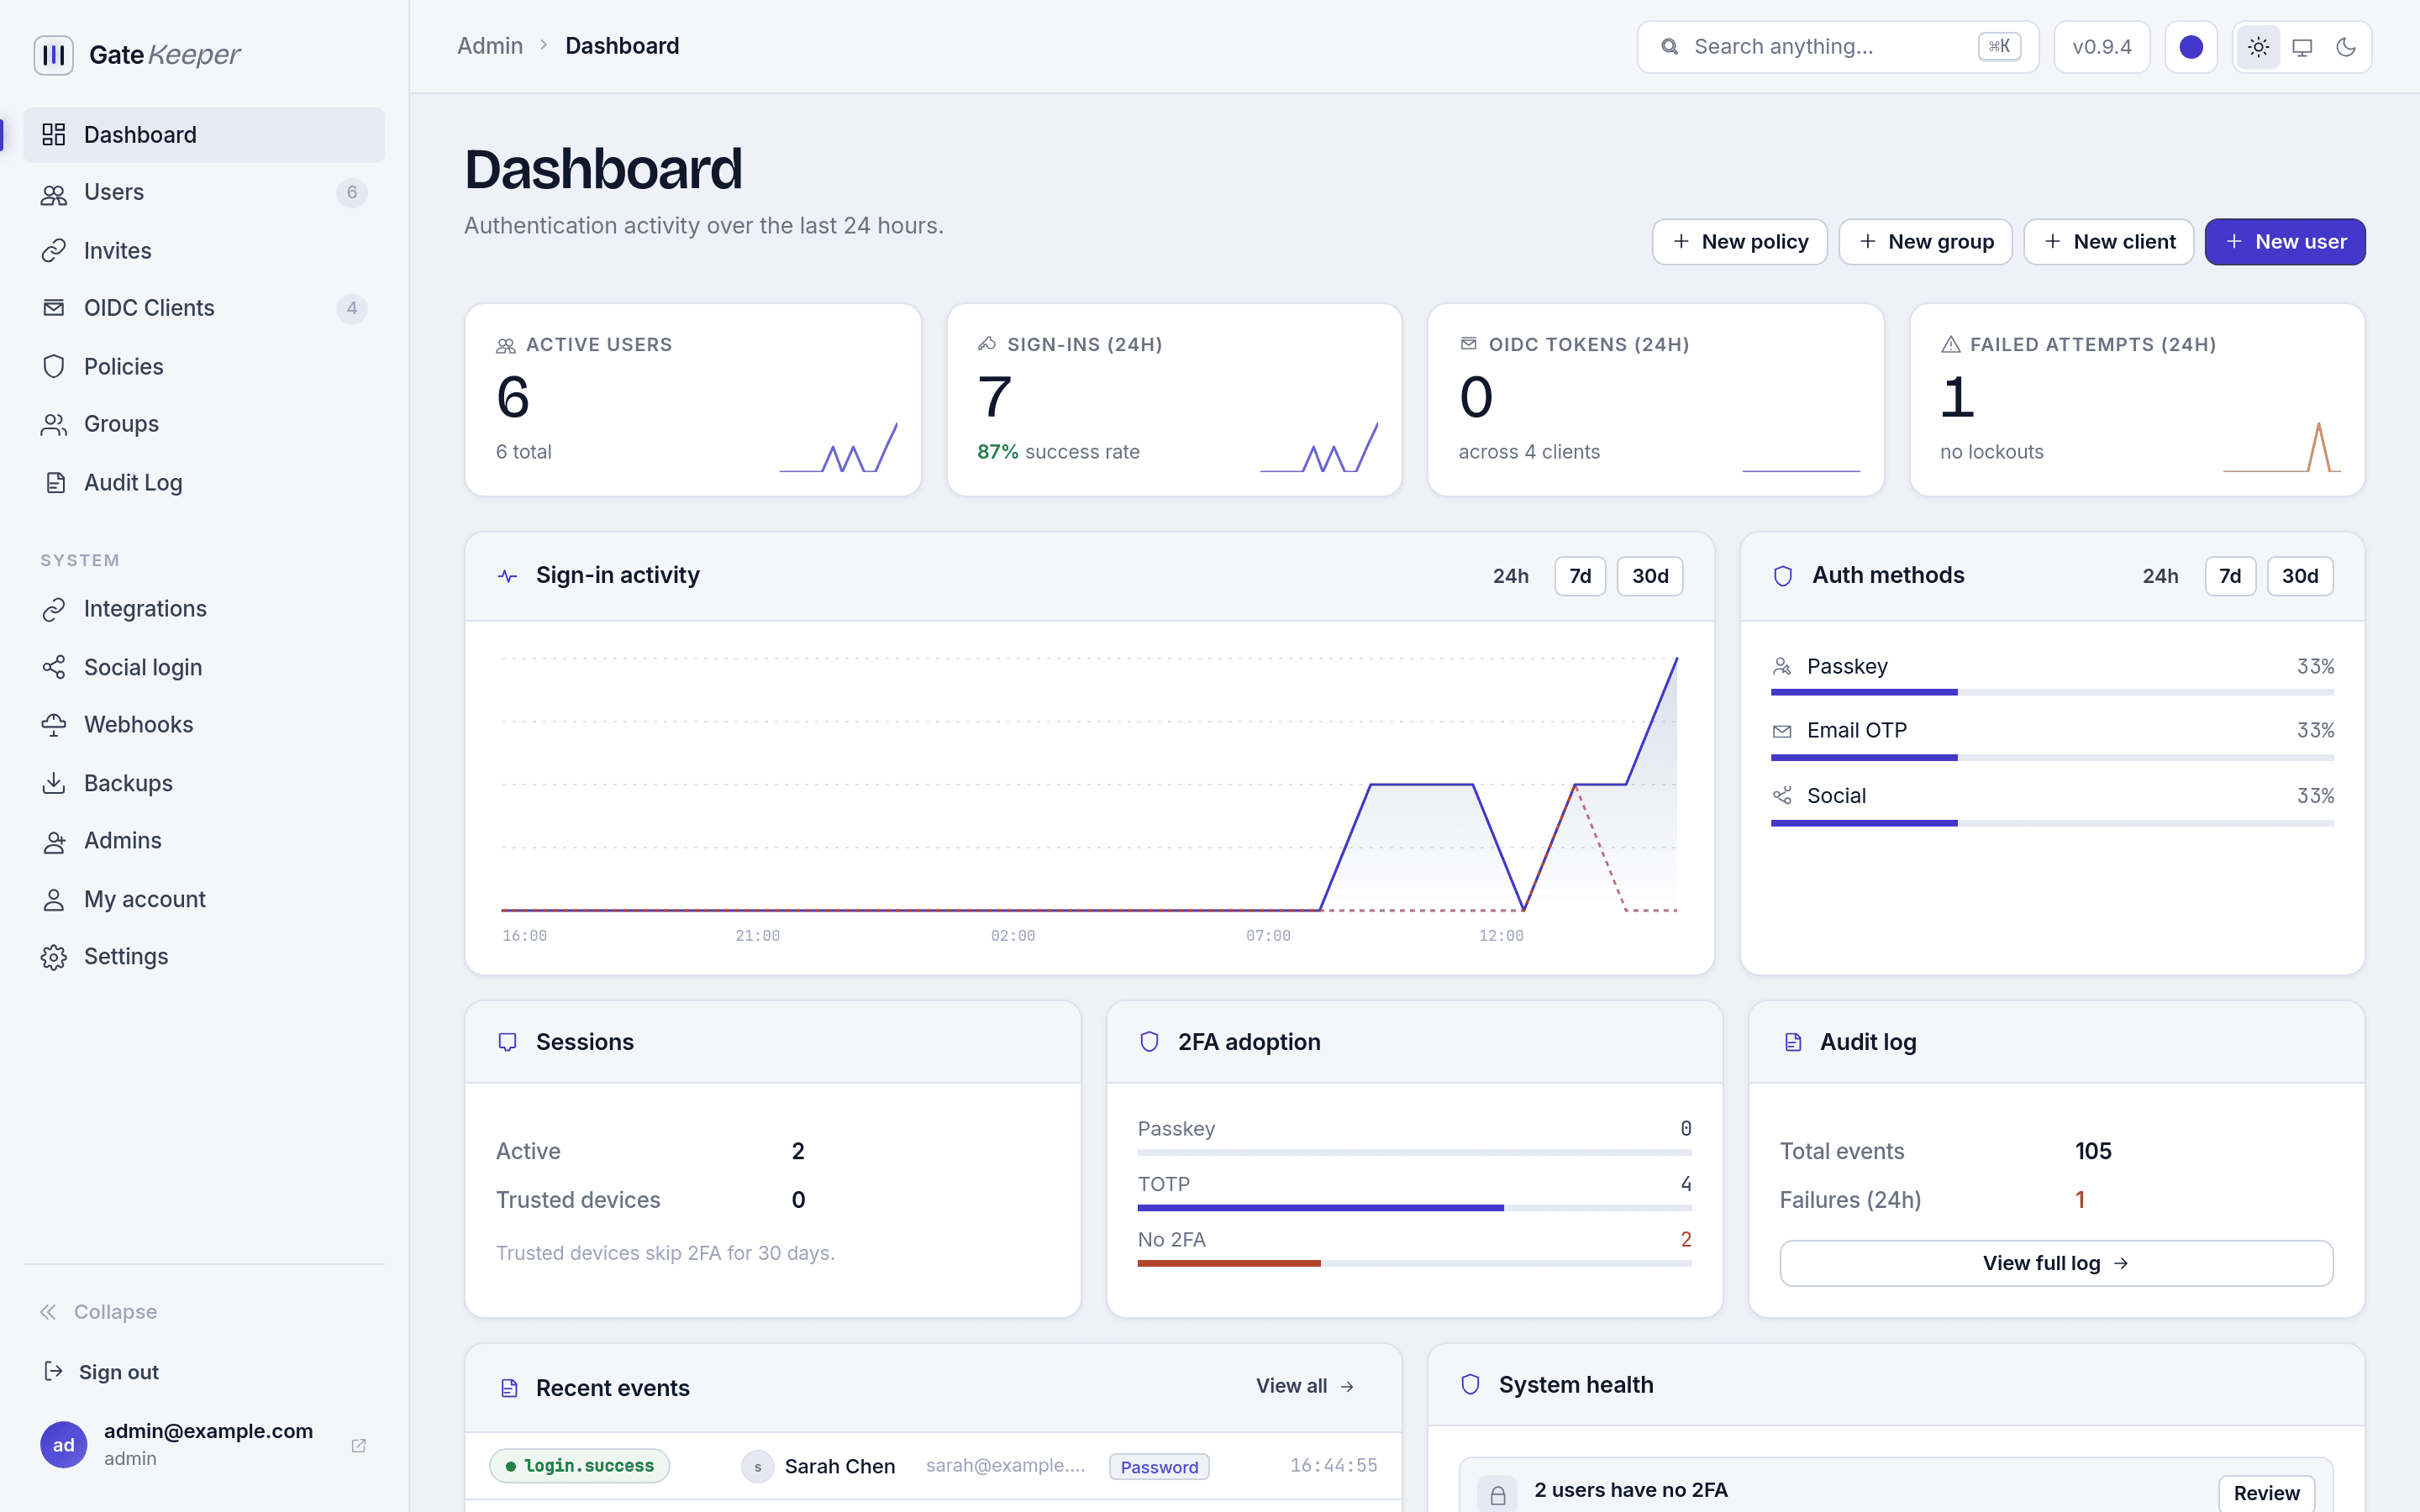
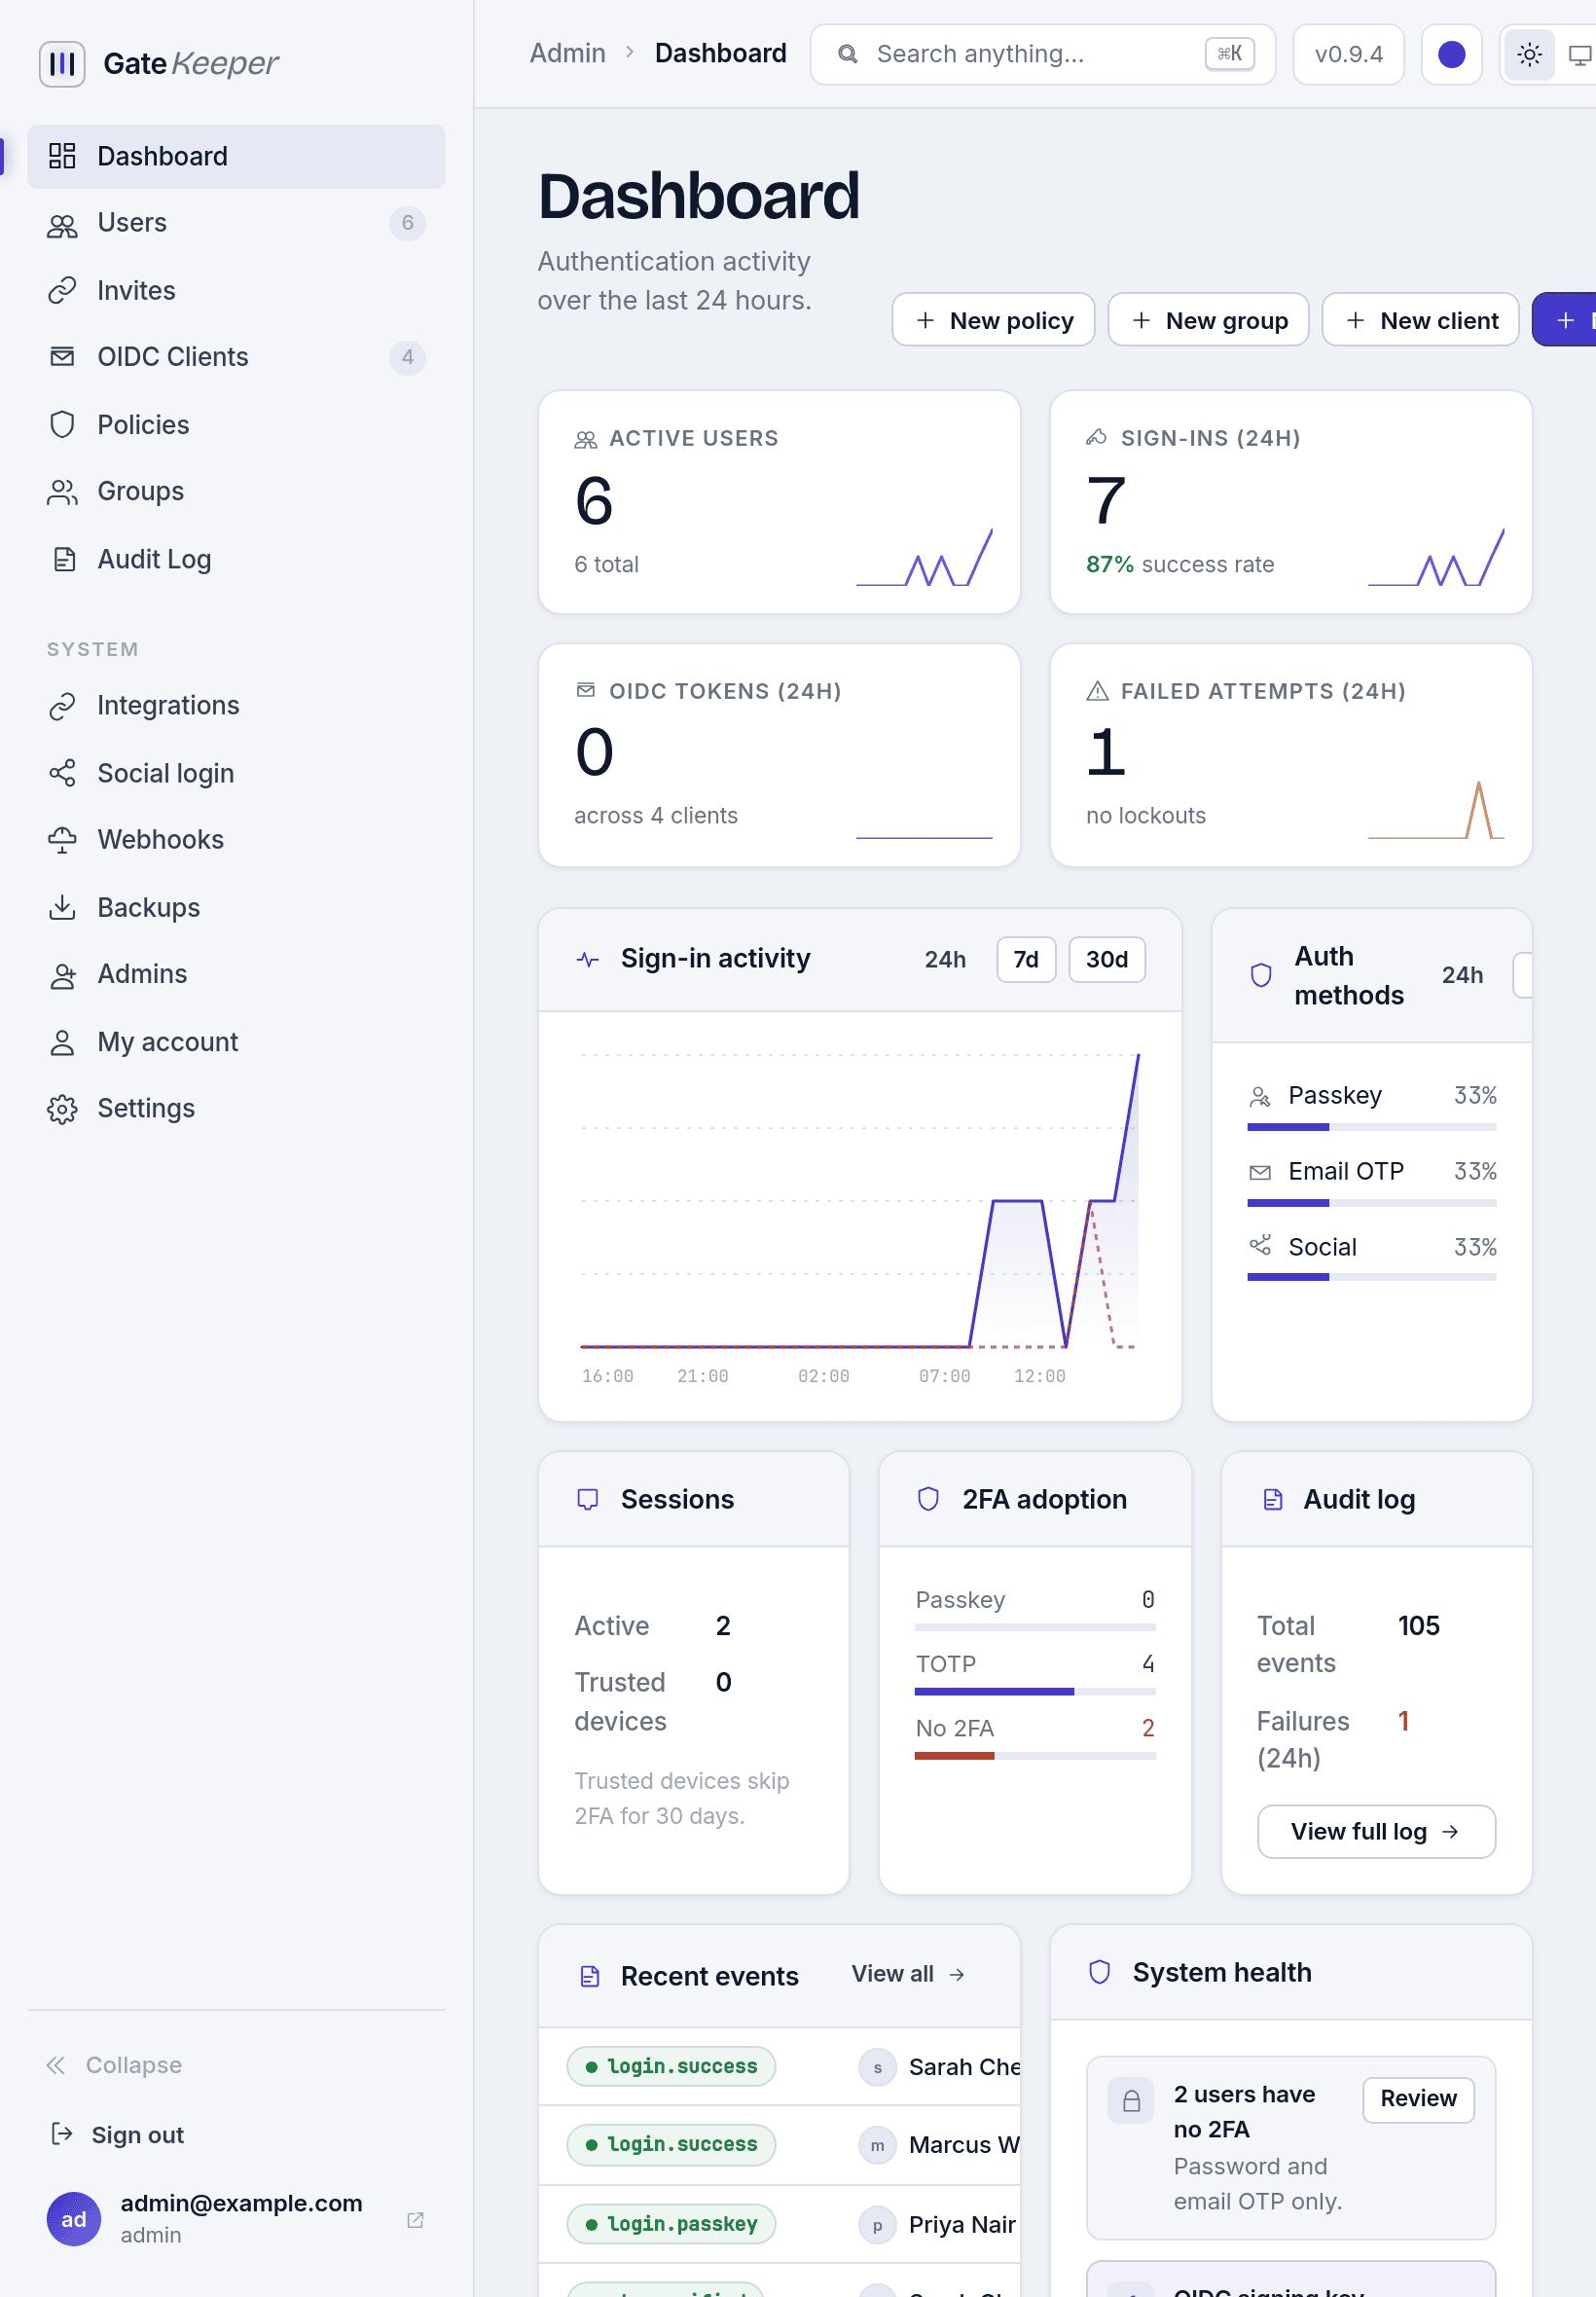
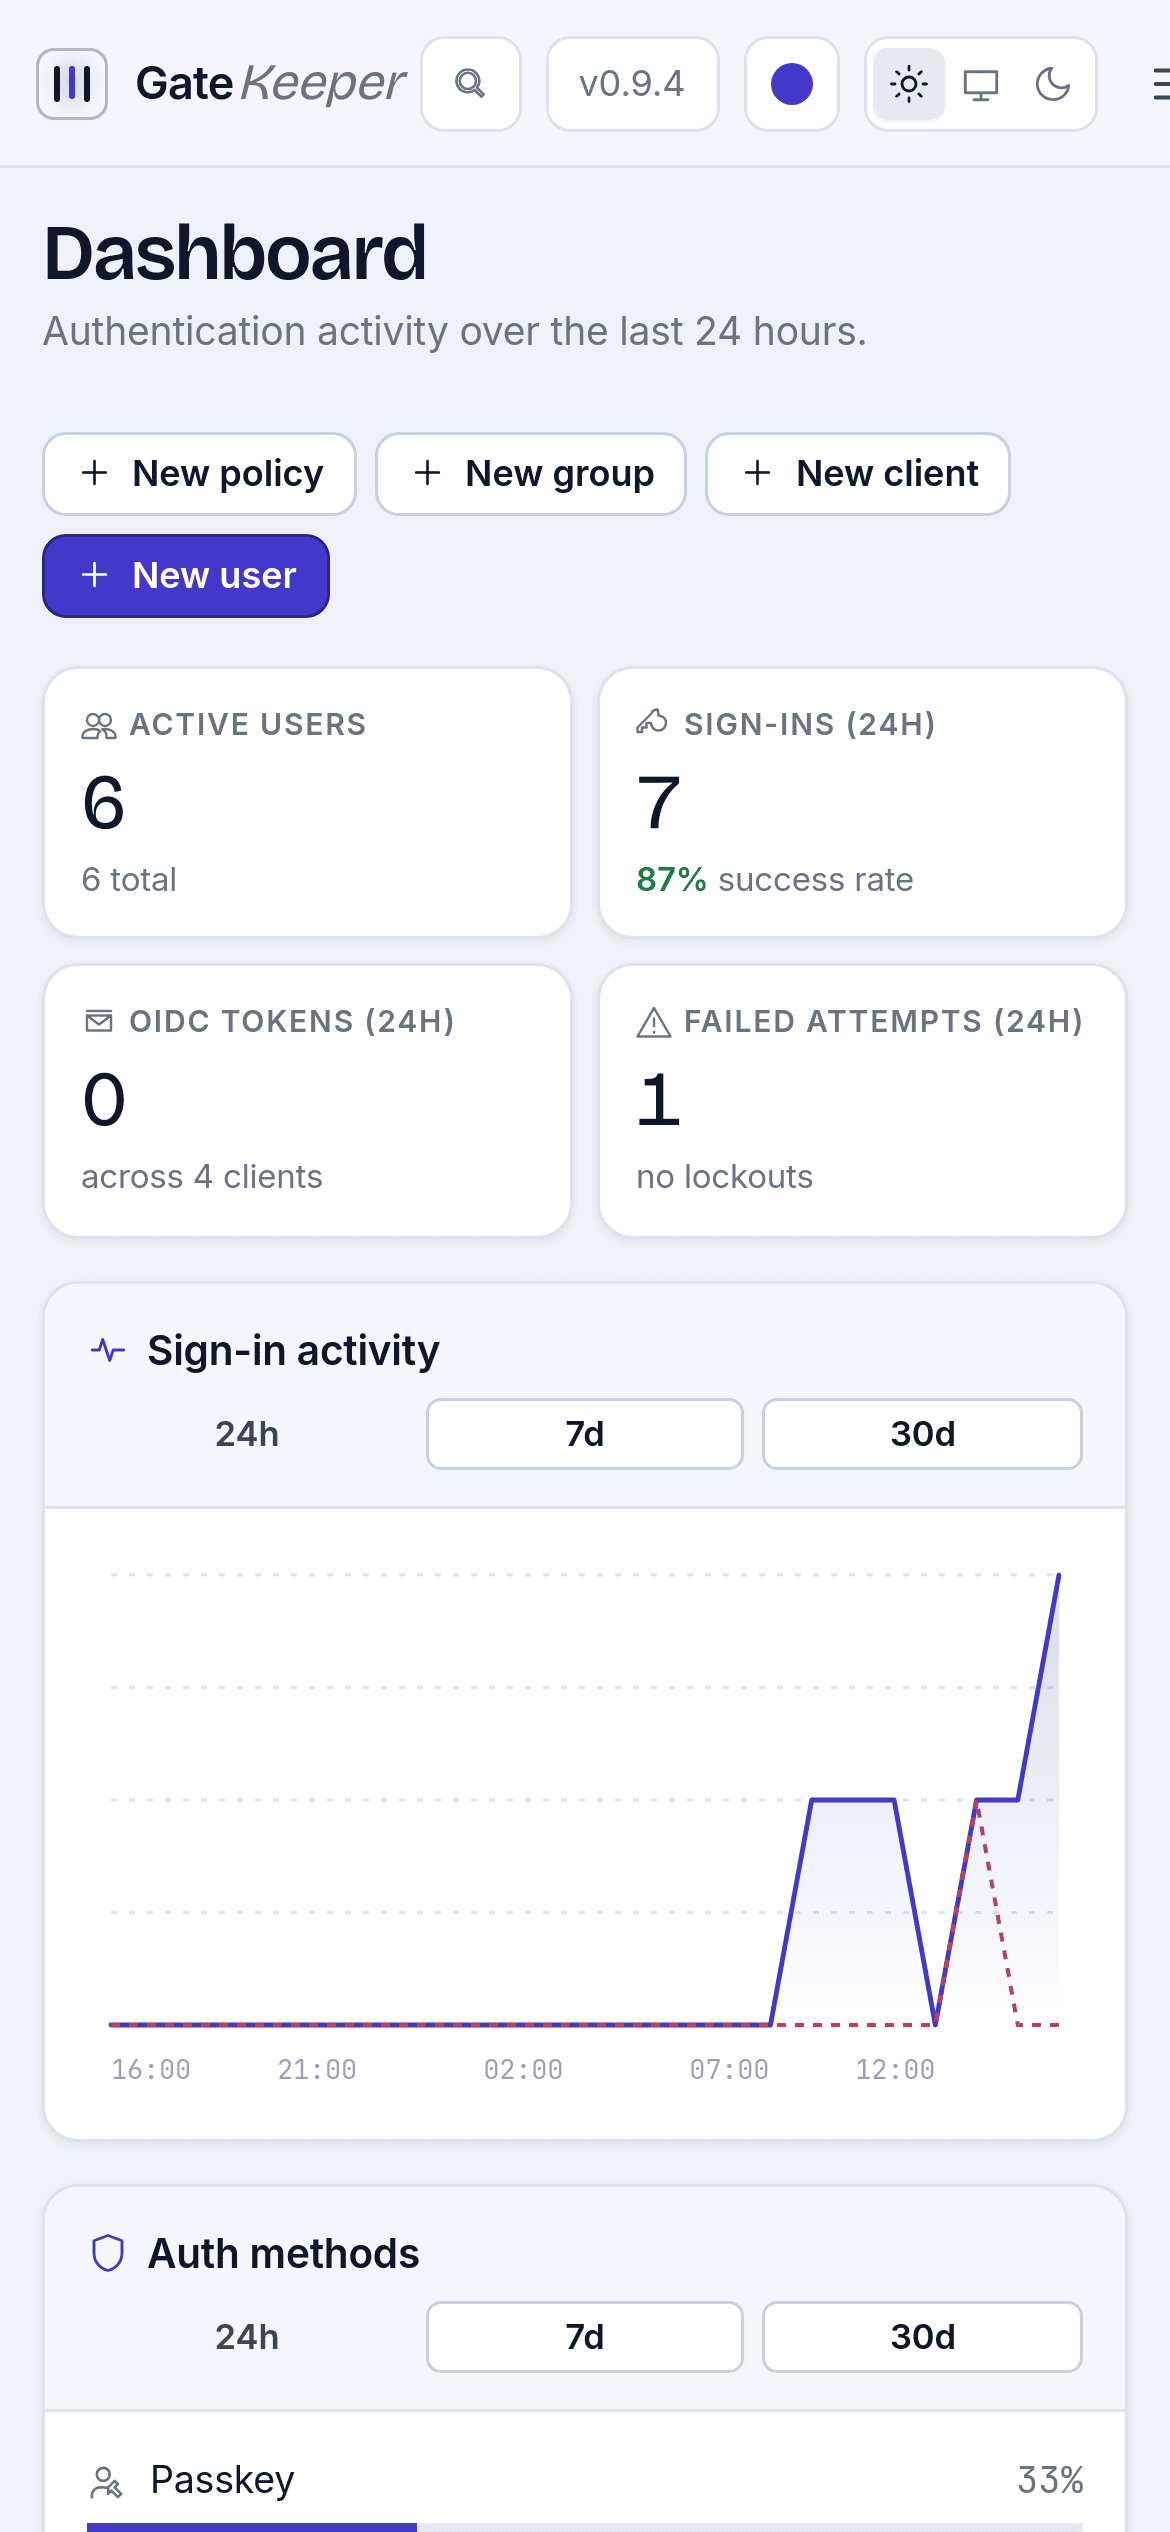
Put a front door on your homelab
One container, a SQLite file, and everything else configured from the admin panel.
docker pull ghcr.io/chr0nzz/gatekeeper:latestFree and open source. If it saves you time, a star goes a long way.
Features
Everything needed to put a single sign-in in front of what you run.
Six ways in, one page
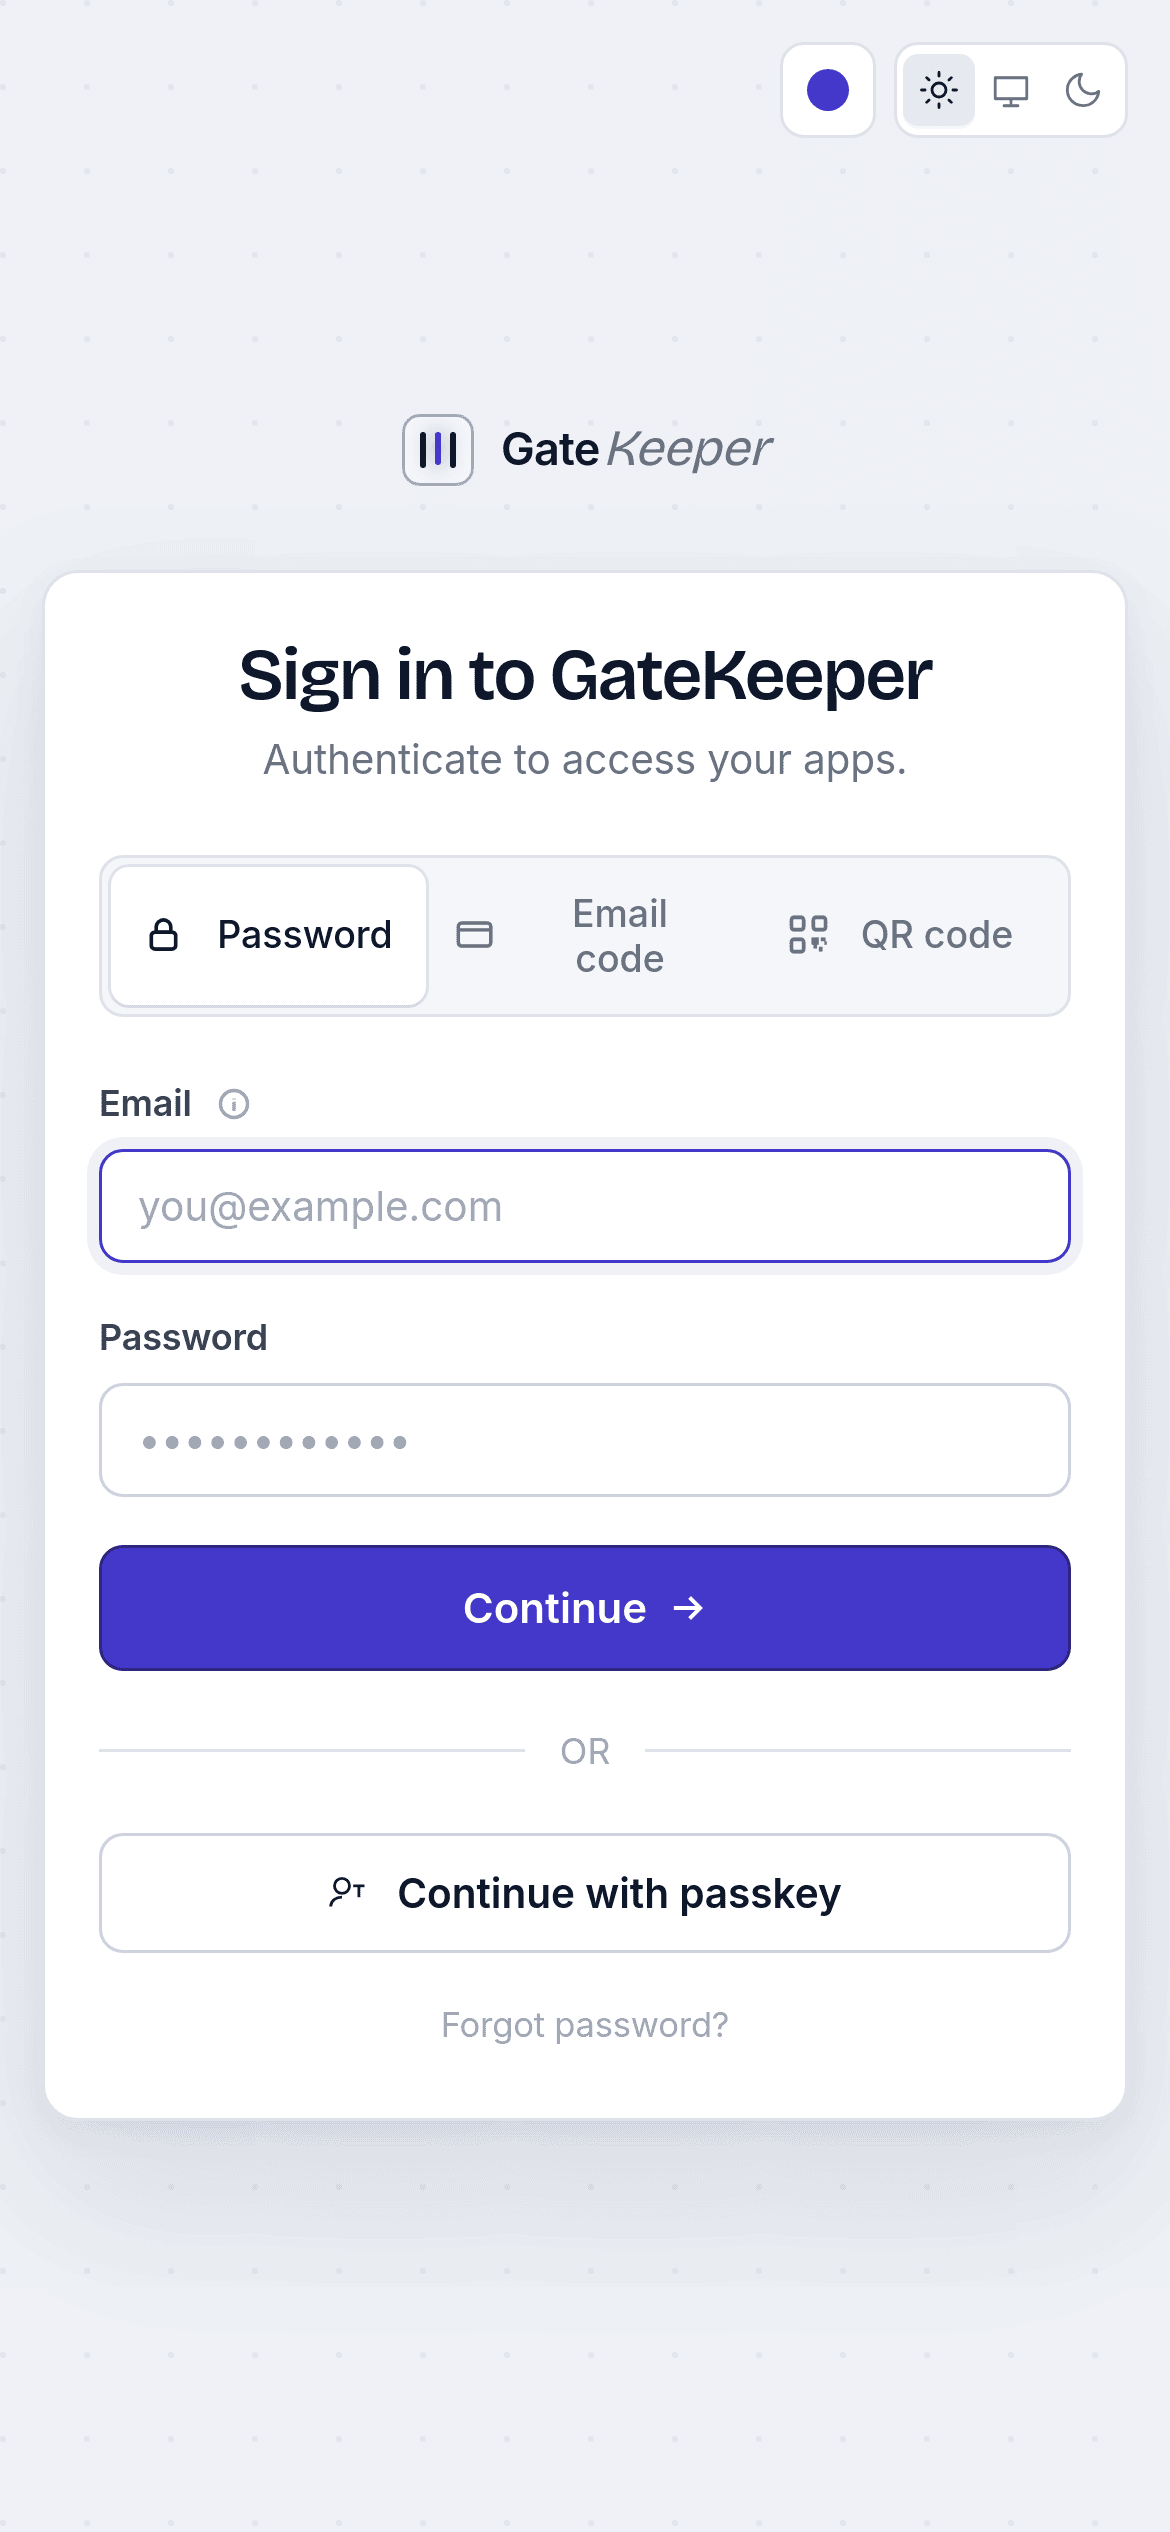
Password with an emailed code, passwordless codes, an authenticator app, a passkey, a QR code scanned with your phone, or GitHub, Google and Discord. When an app starts the sign-in, its own name and icon appear on the page.
Explore Sign-in →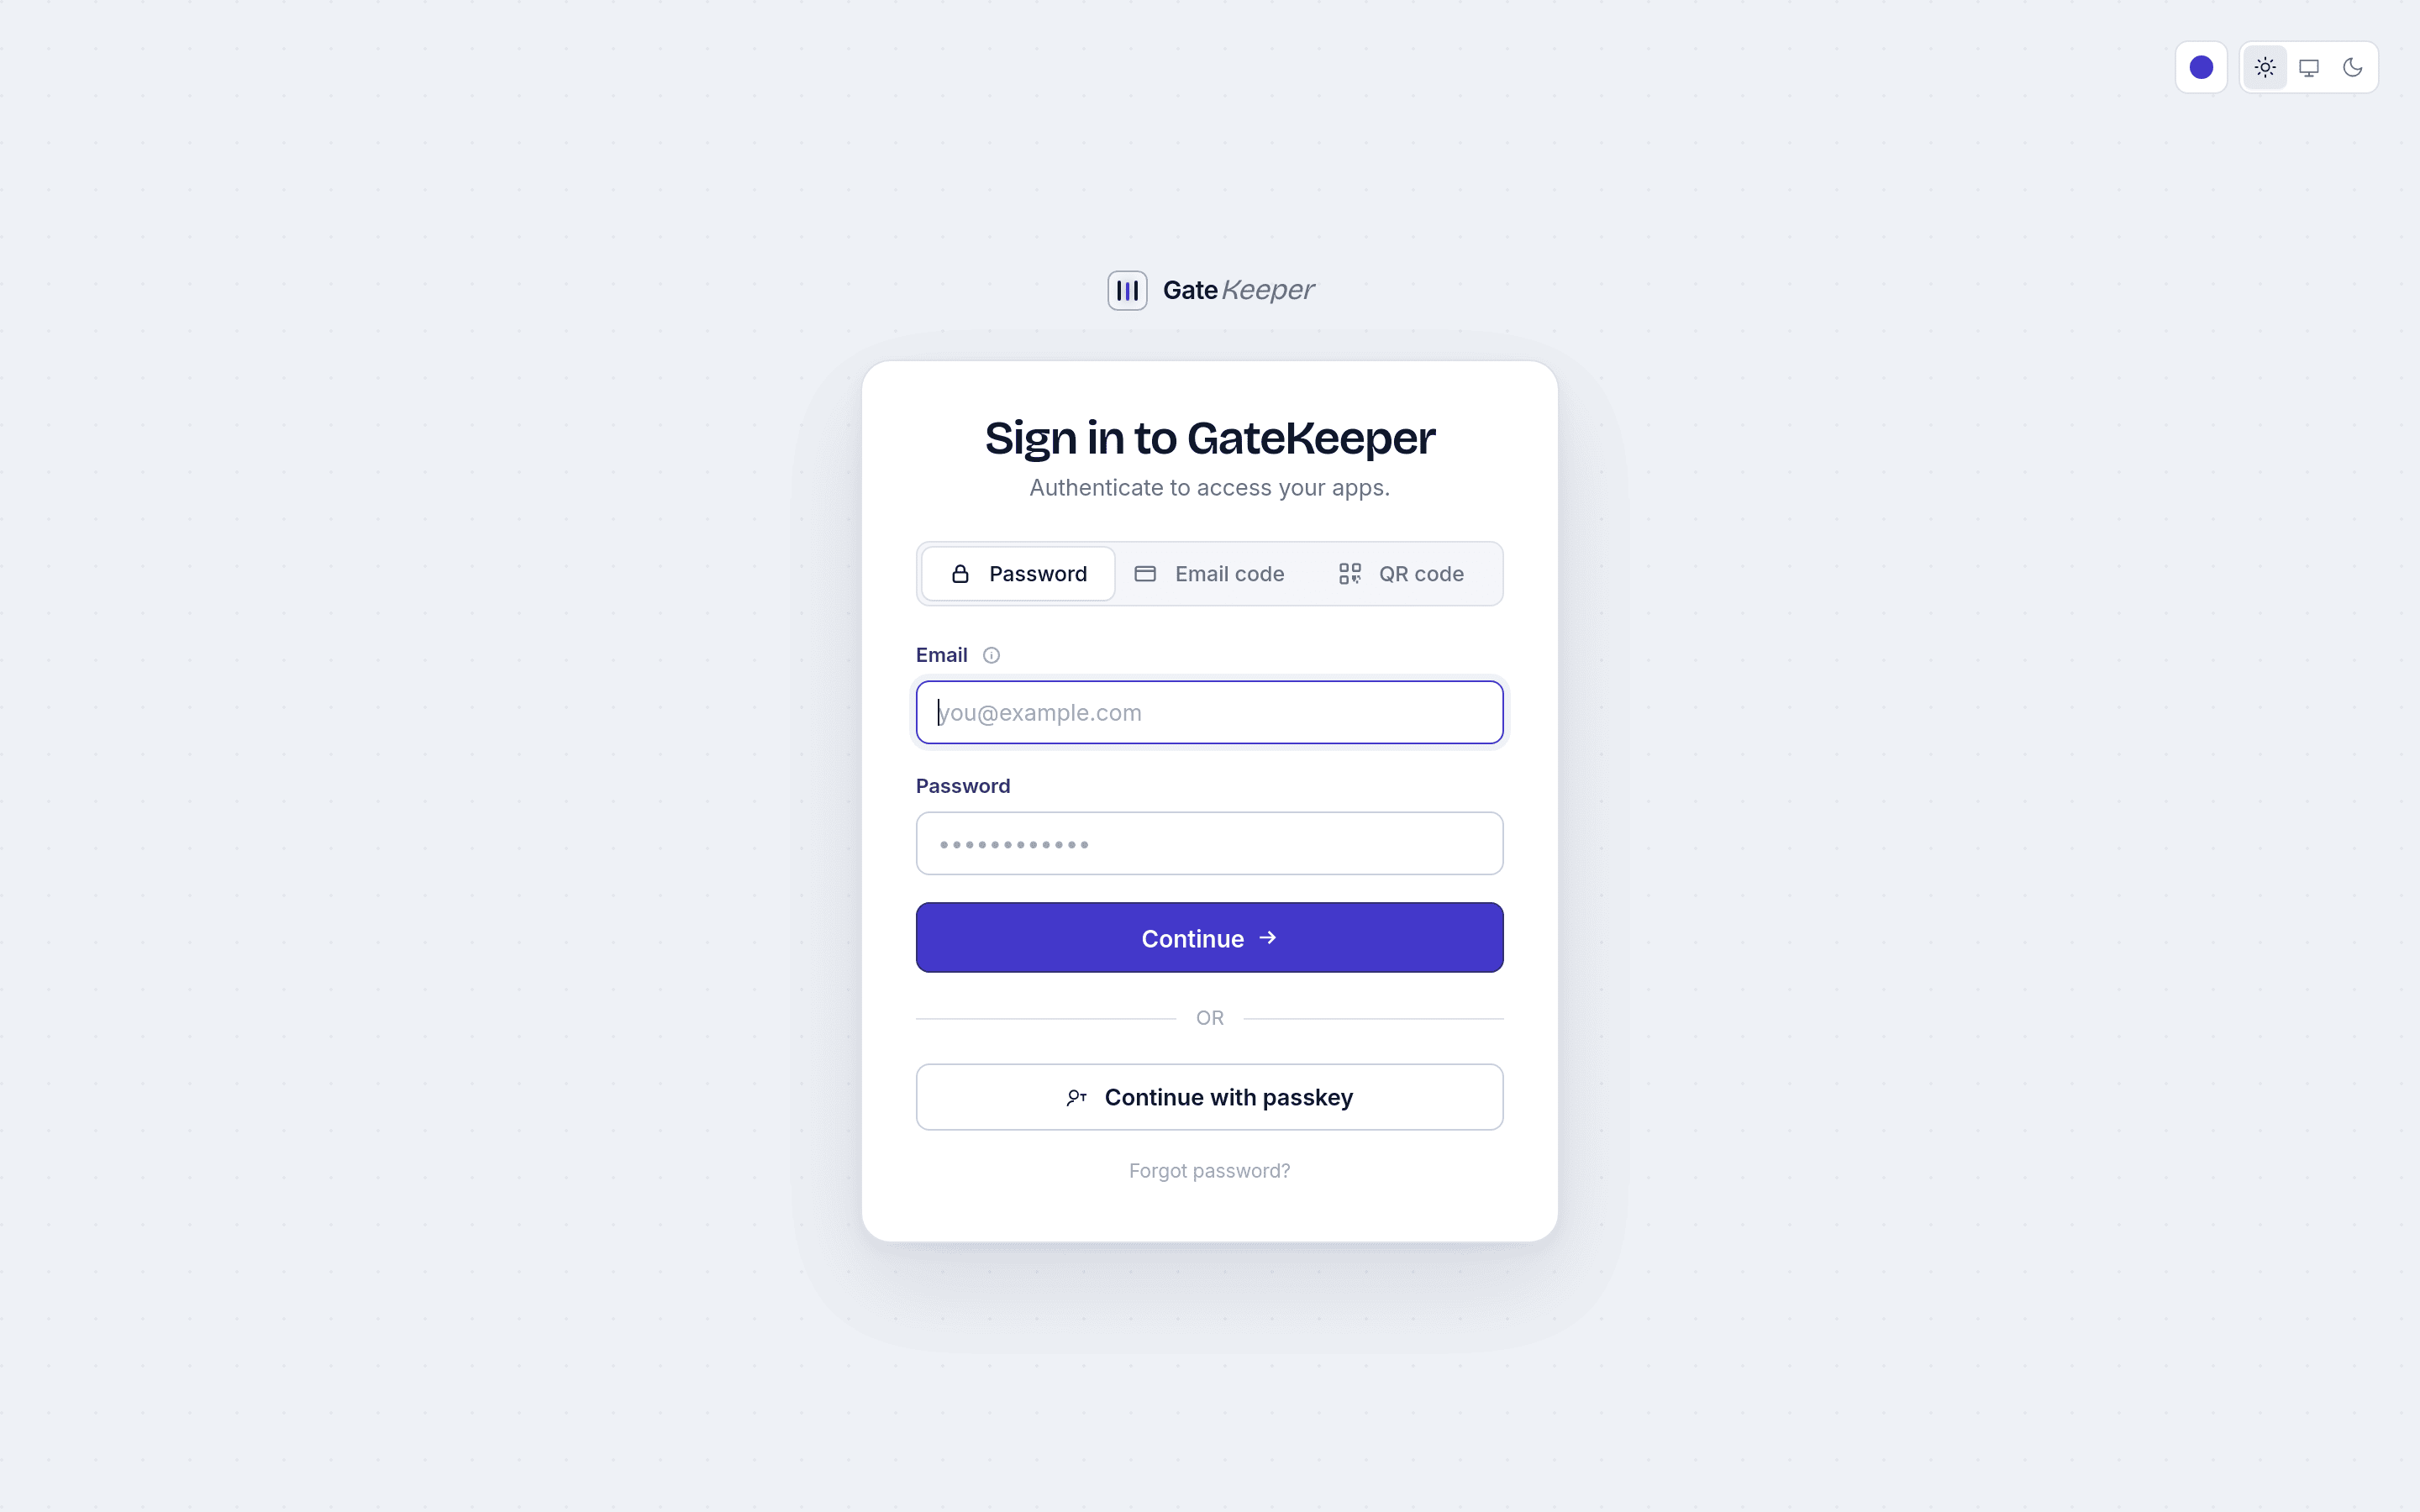
See what is happening right now
Live sign-in activity, failed attempts, token counts and two-factor adoption, with a health panel that surfaces the accounts and settings that need attention.
Explore Dashboard →An identity provider for every app
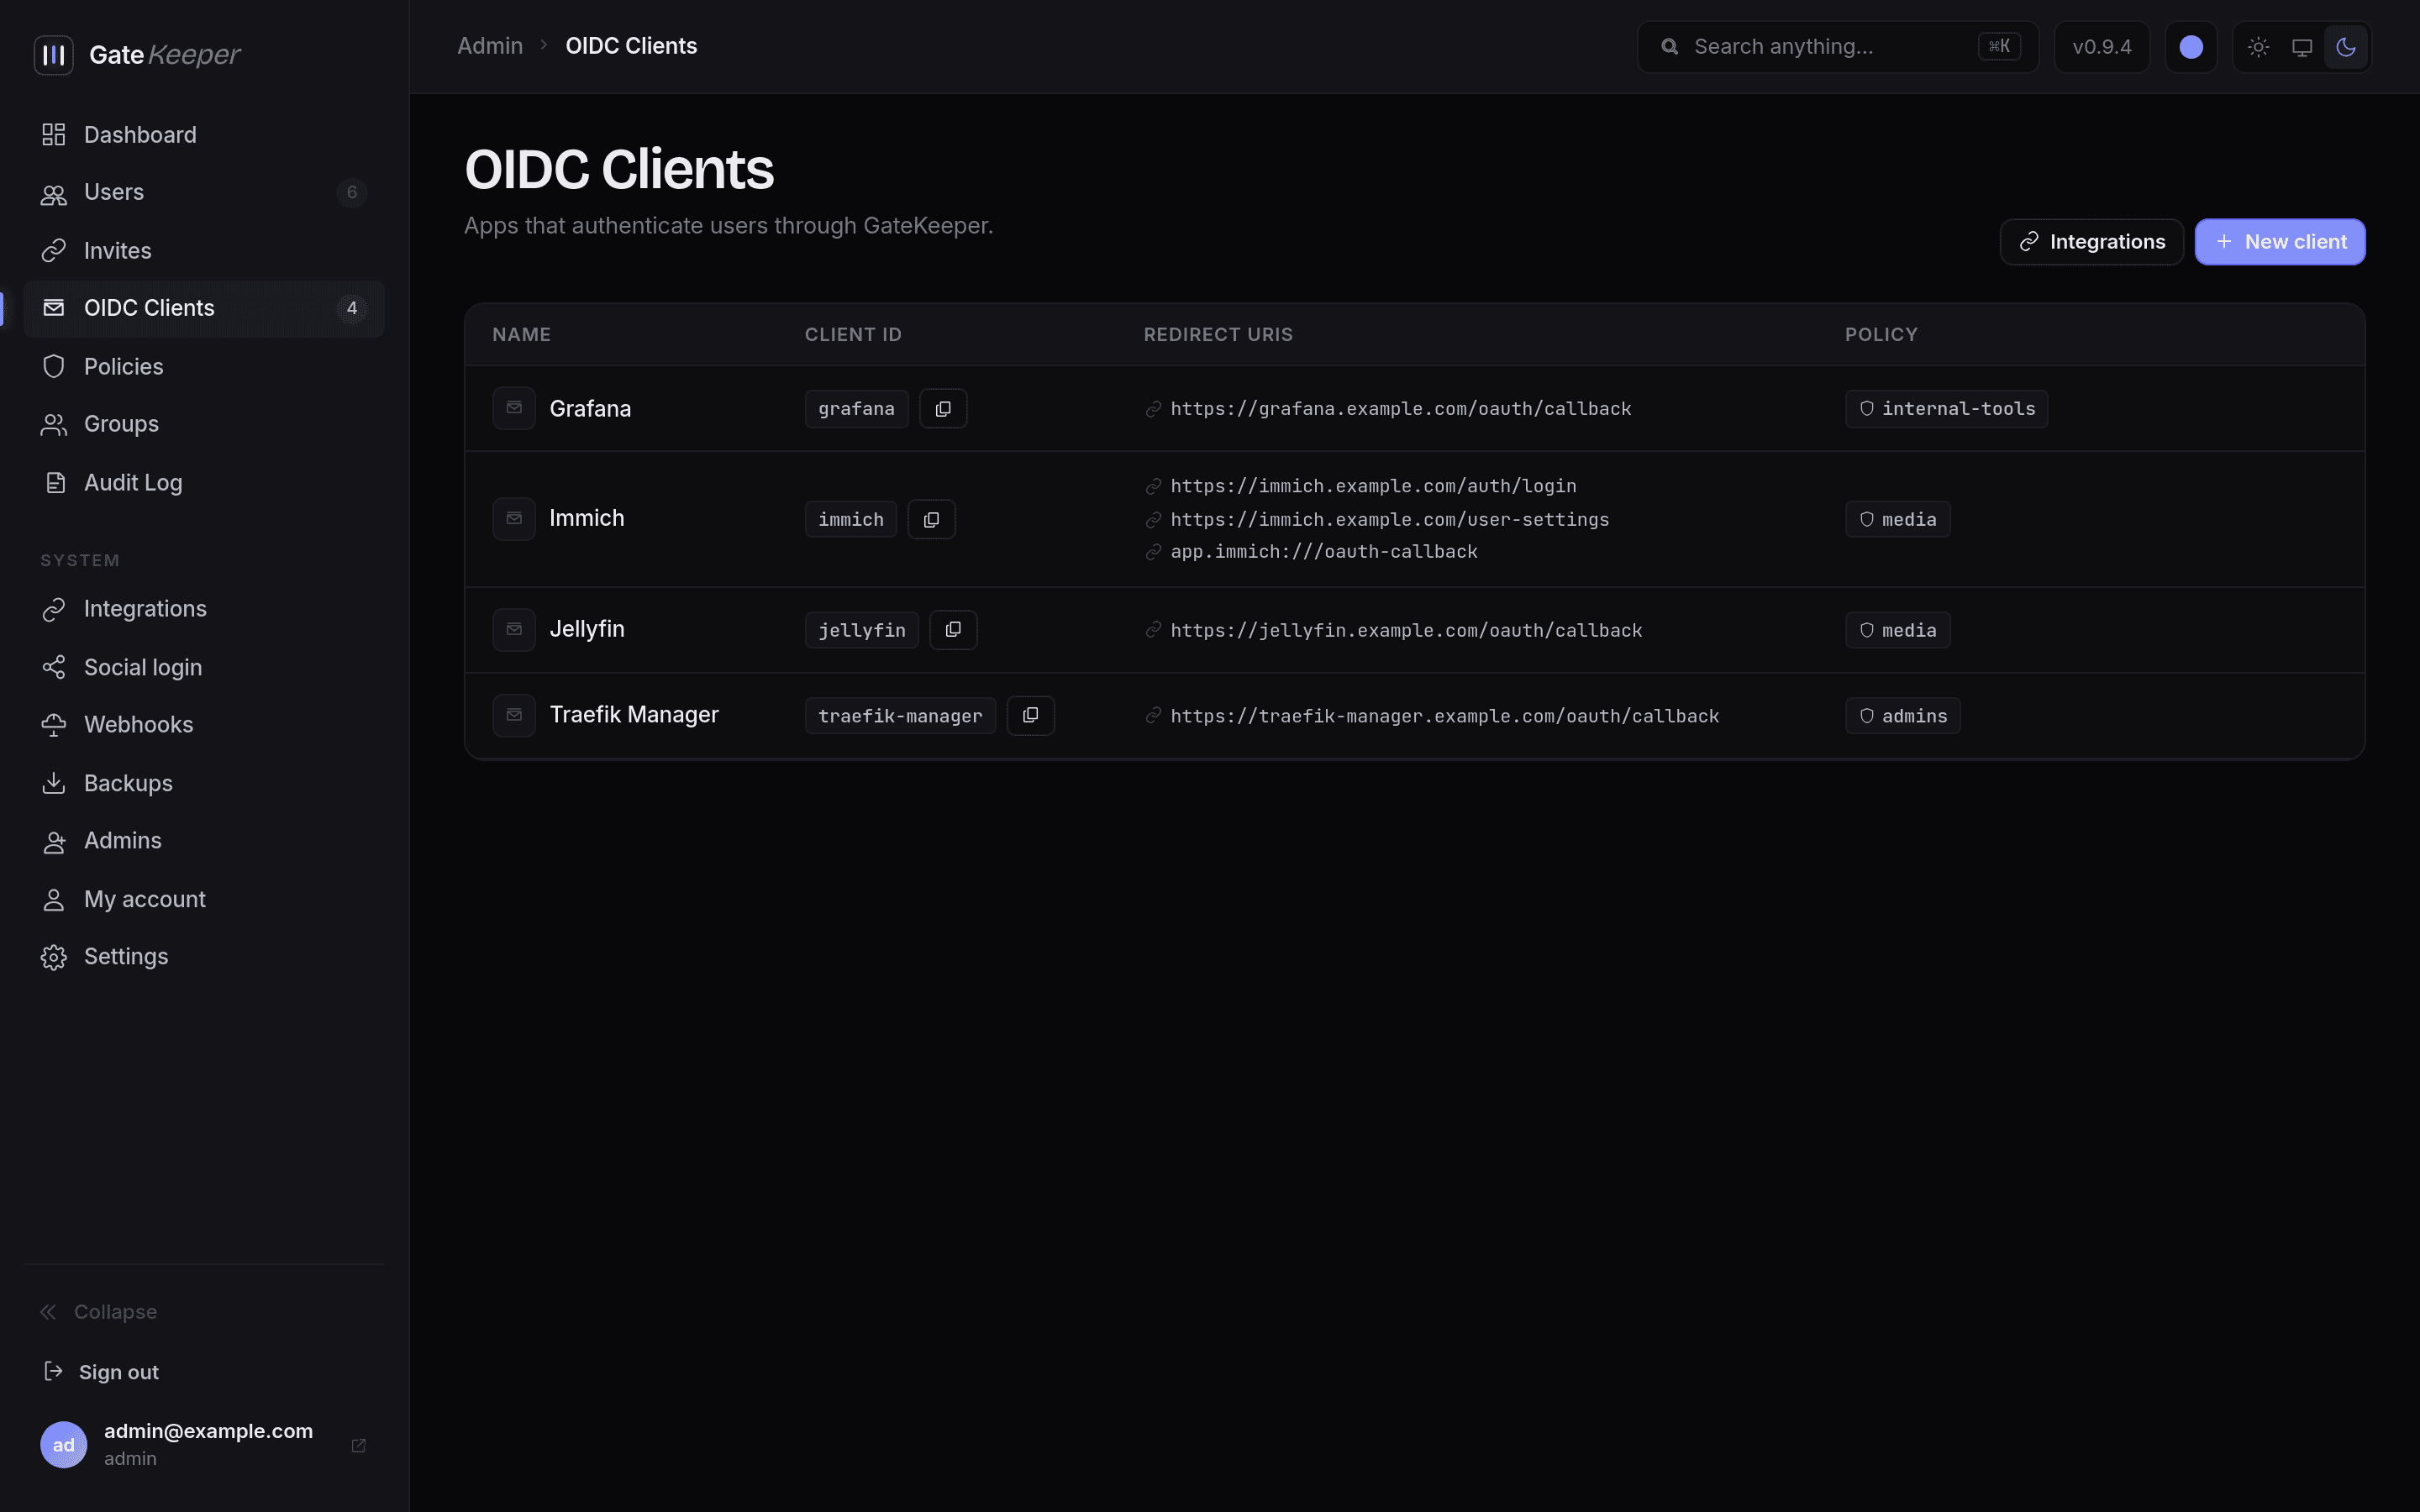
Register a client and any app that speaks OpenID Connect can hand sign-in to GateKeeper. Authorization code with PKCE, RS256 tokens, group claims for role mapping, and custom claims per client. Mobile apps work too.
Explore OIDC →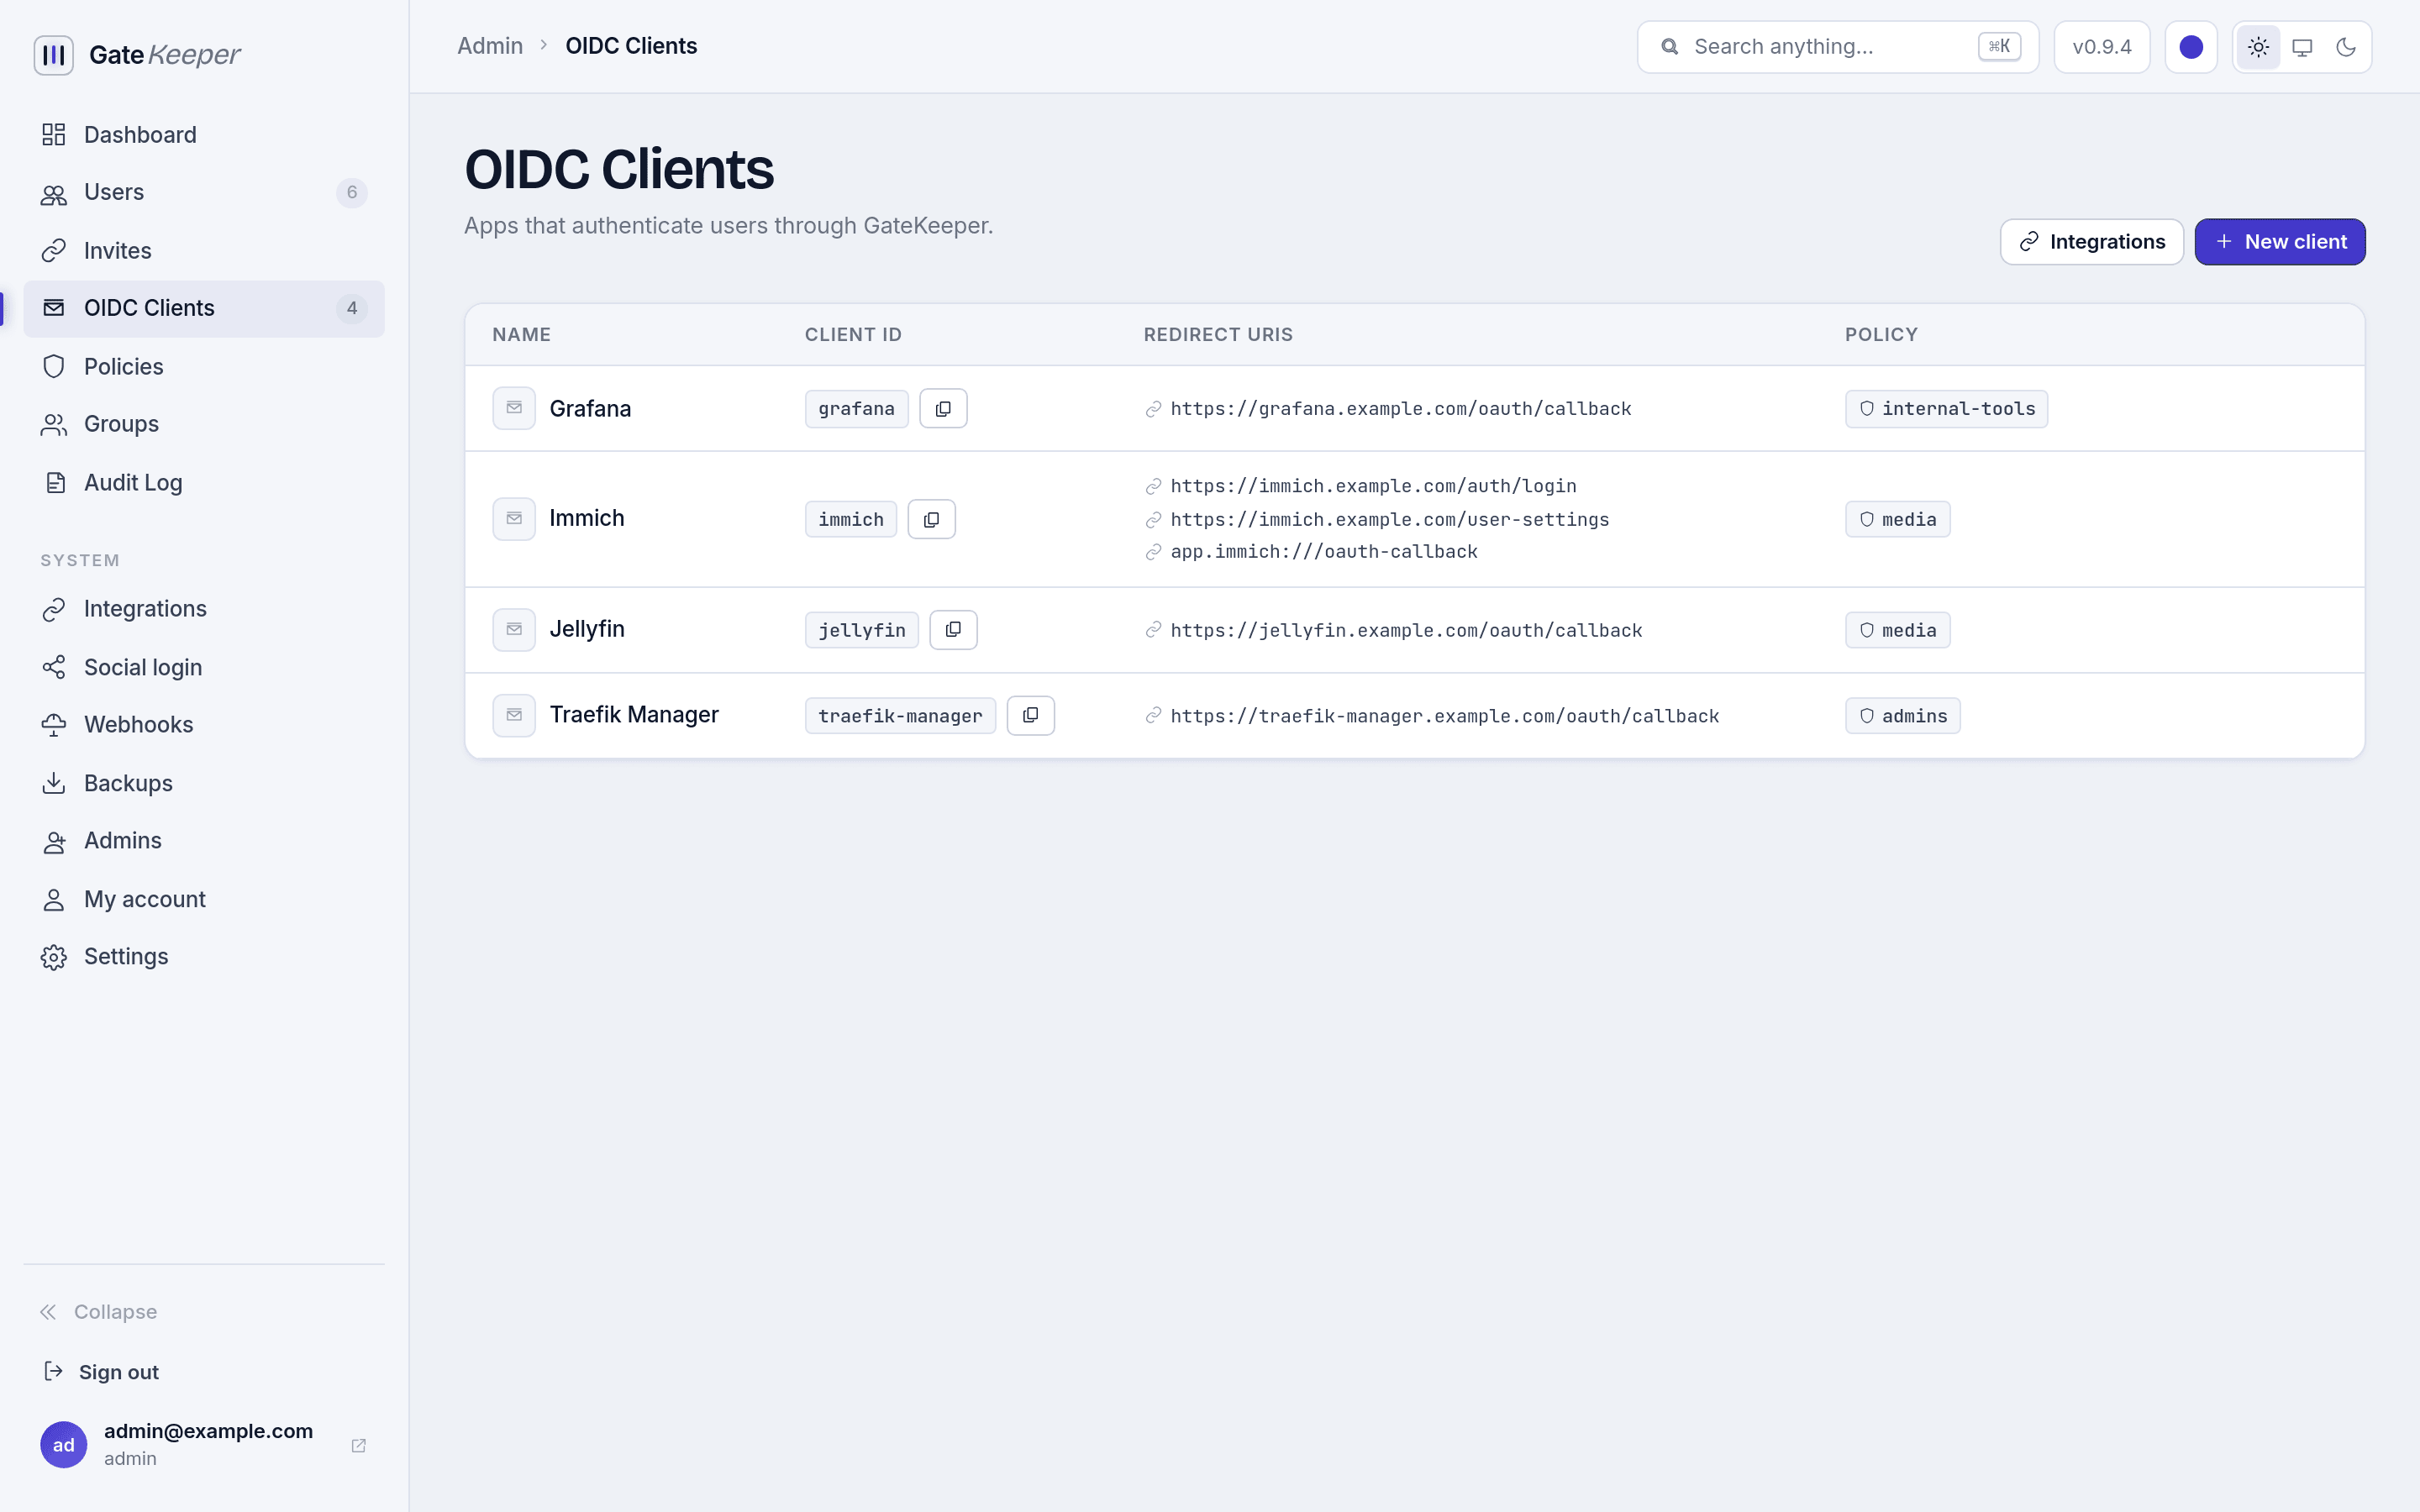
Decide who reaches which app
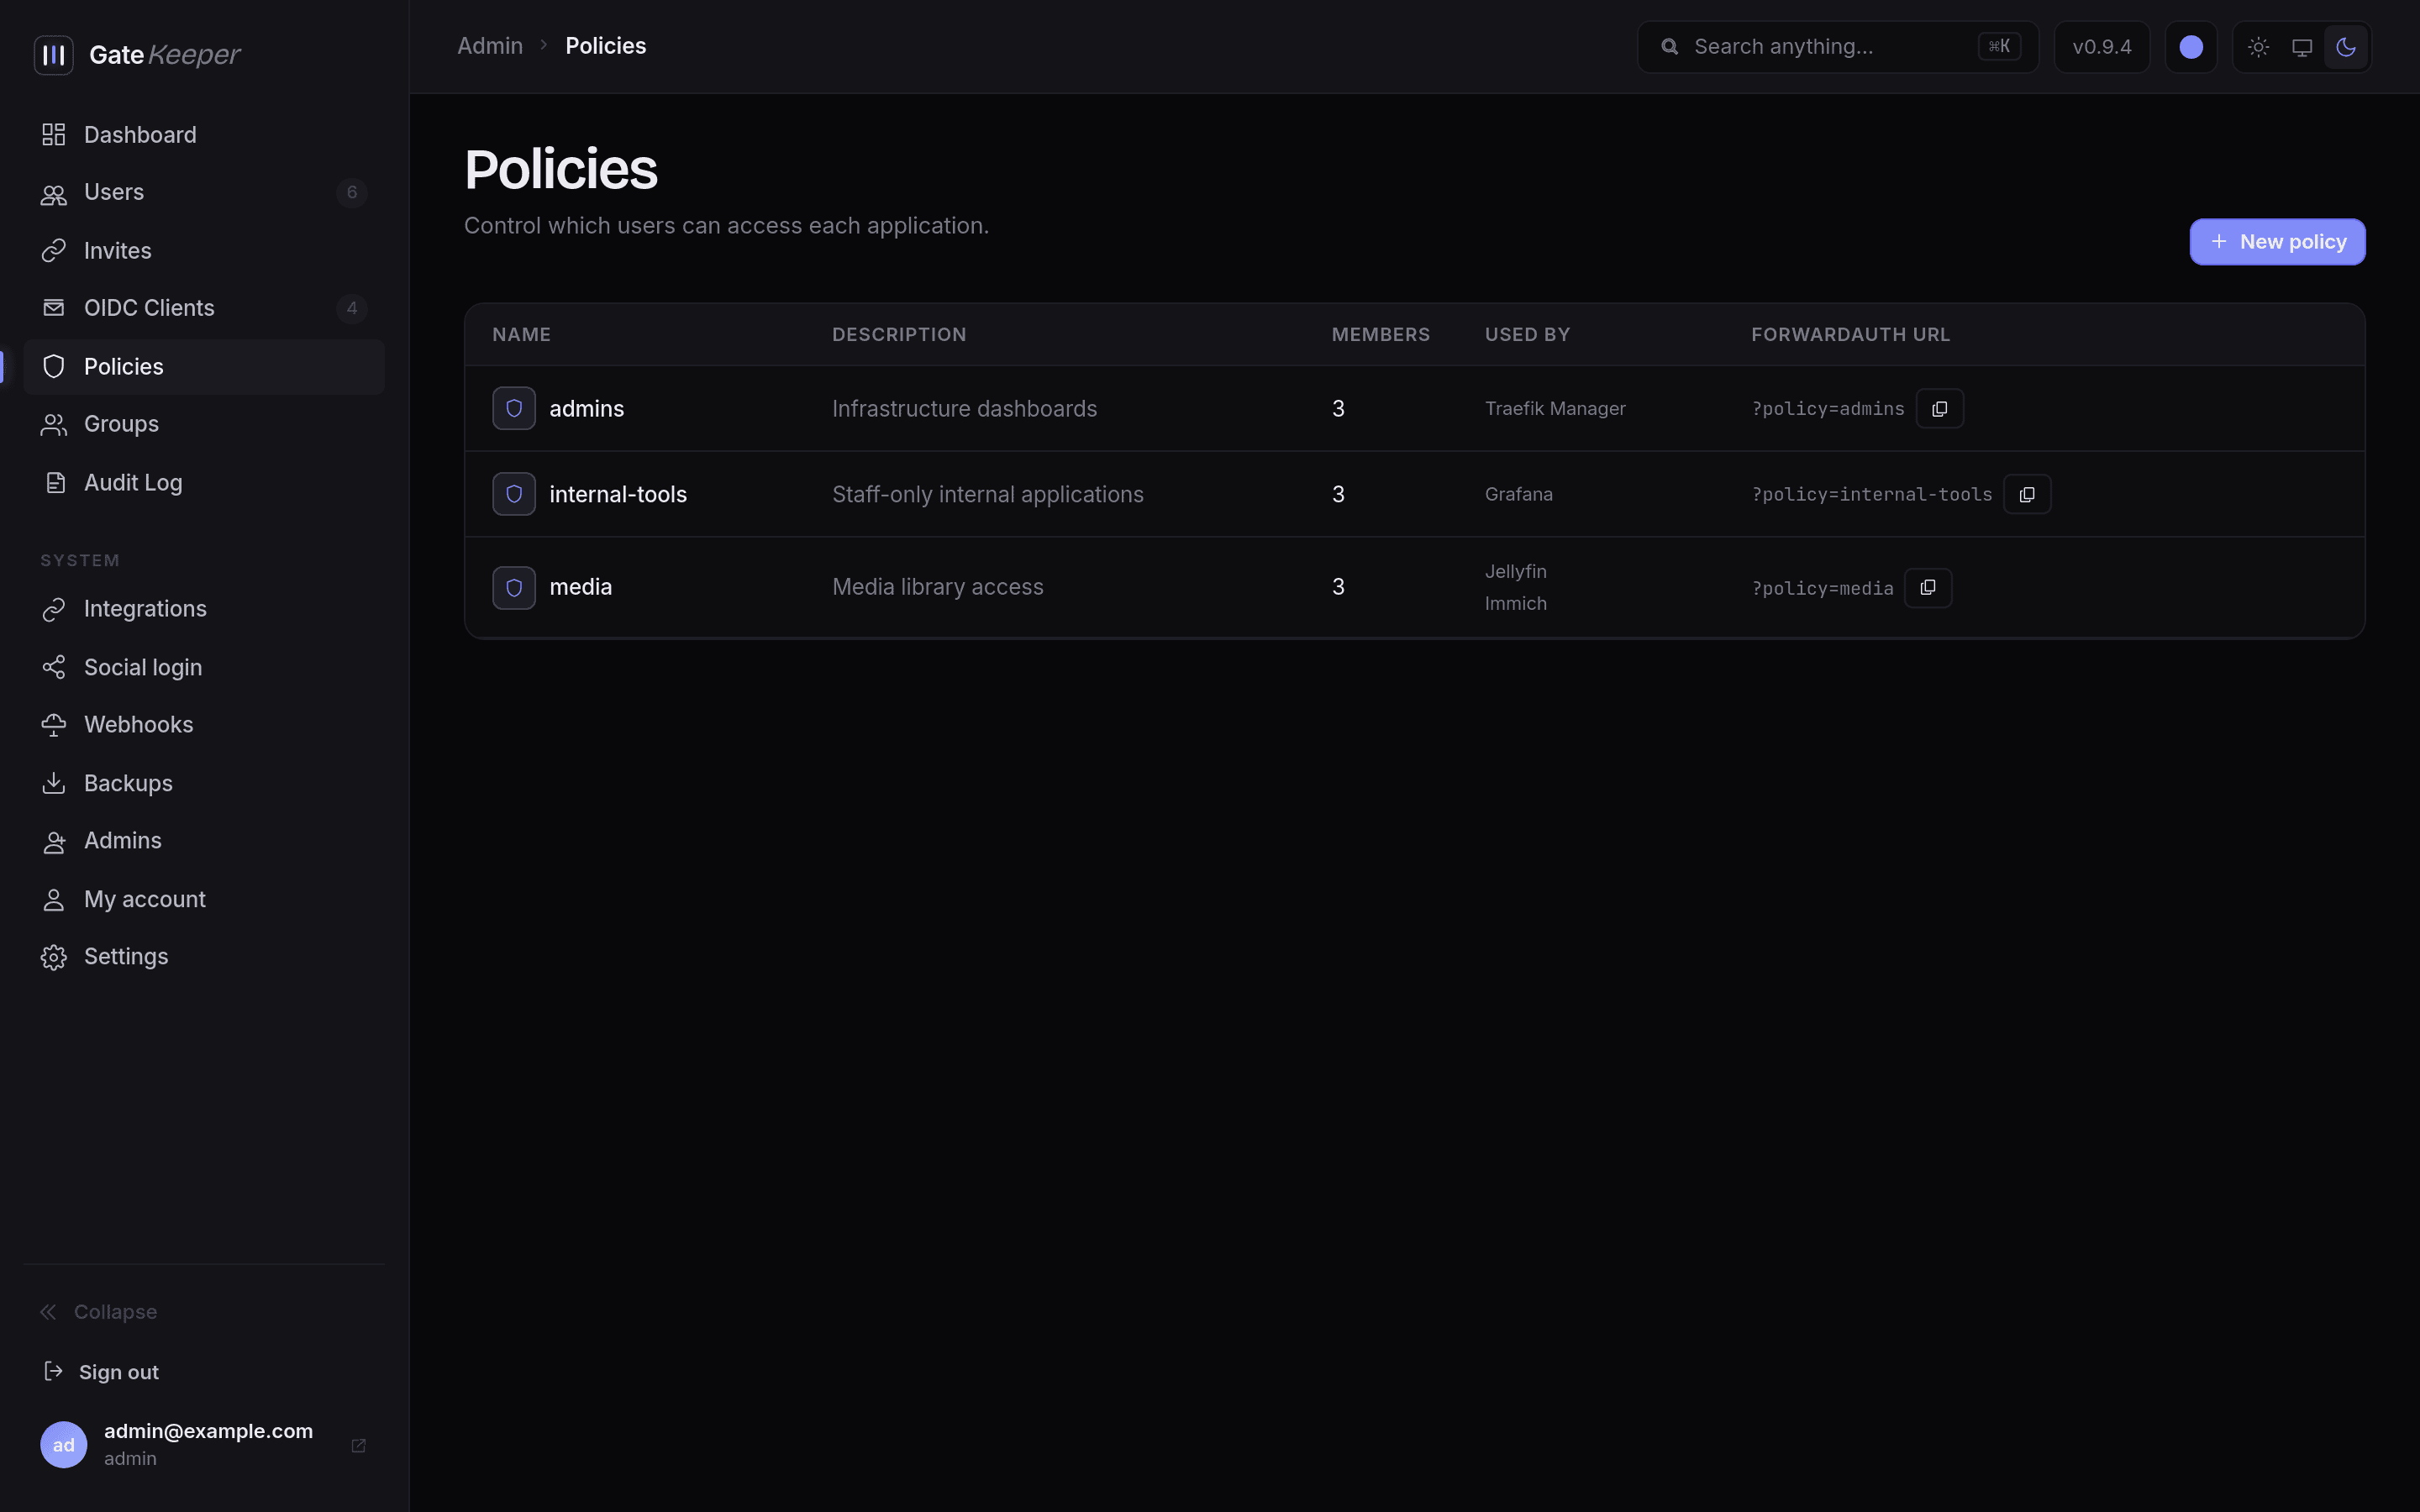
Named policies control access per application, whether it signs in through OIDC or sits behind your reverse proxy. For apps with no sign-in of their own, stored credentials are injected on the way through.
Explore Policies →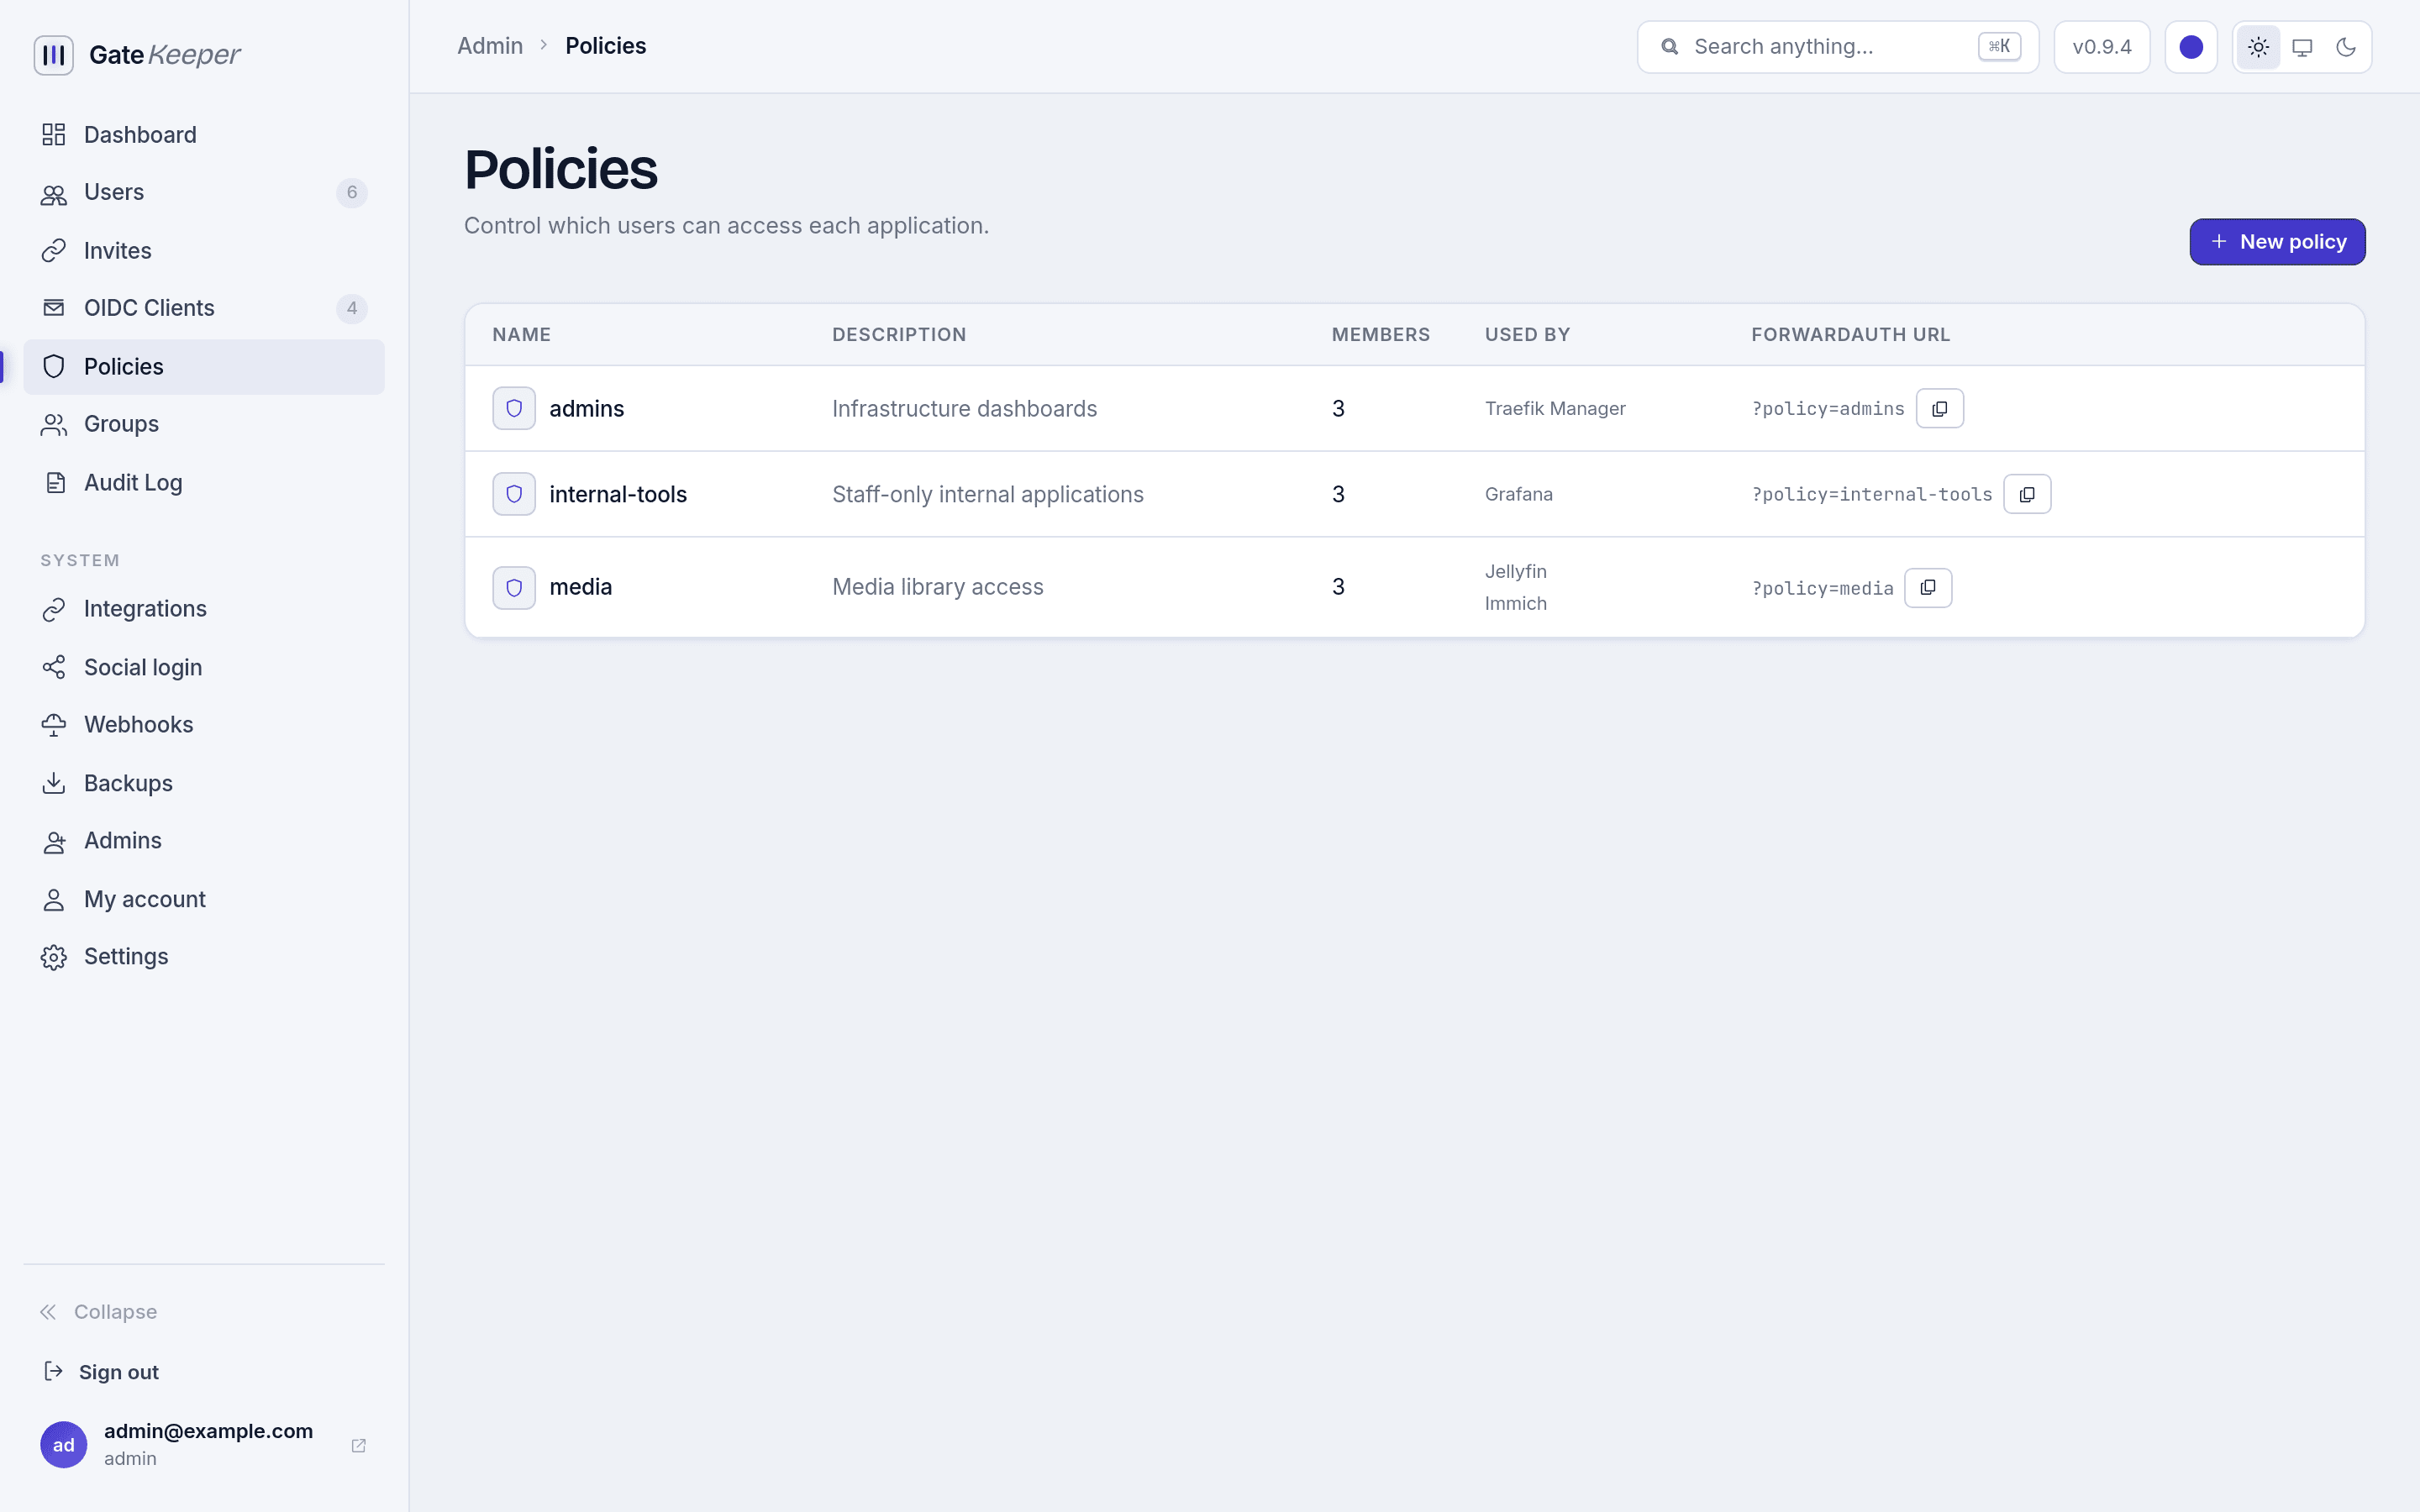
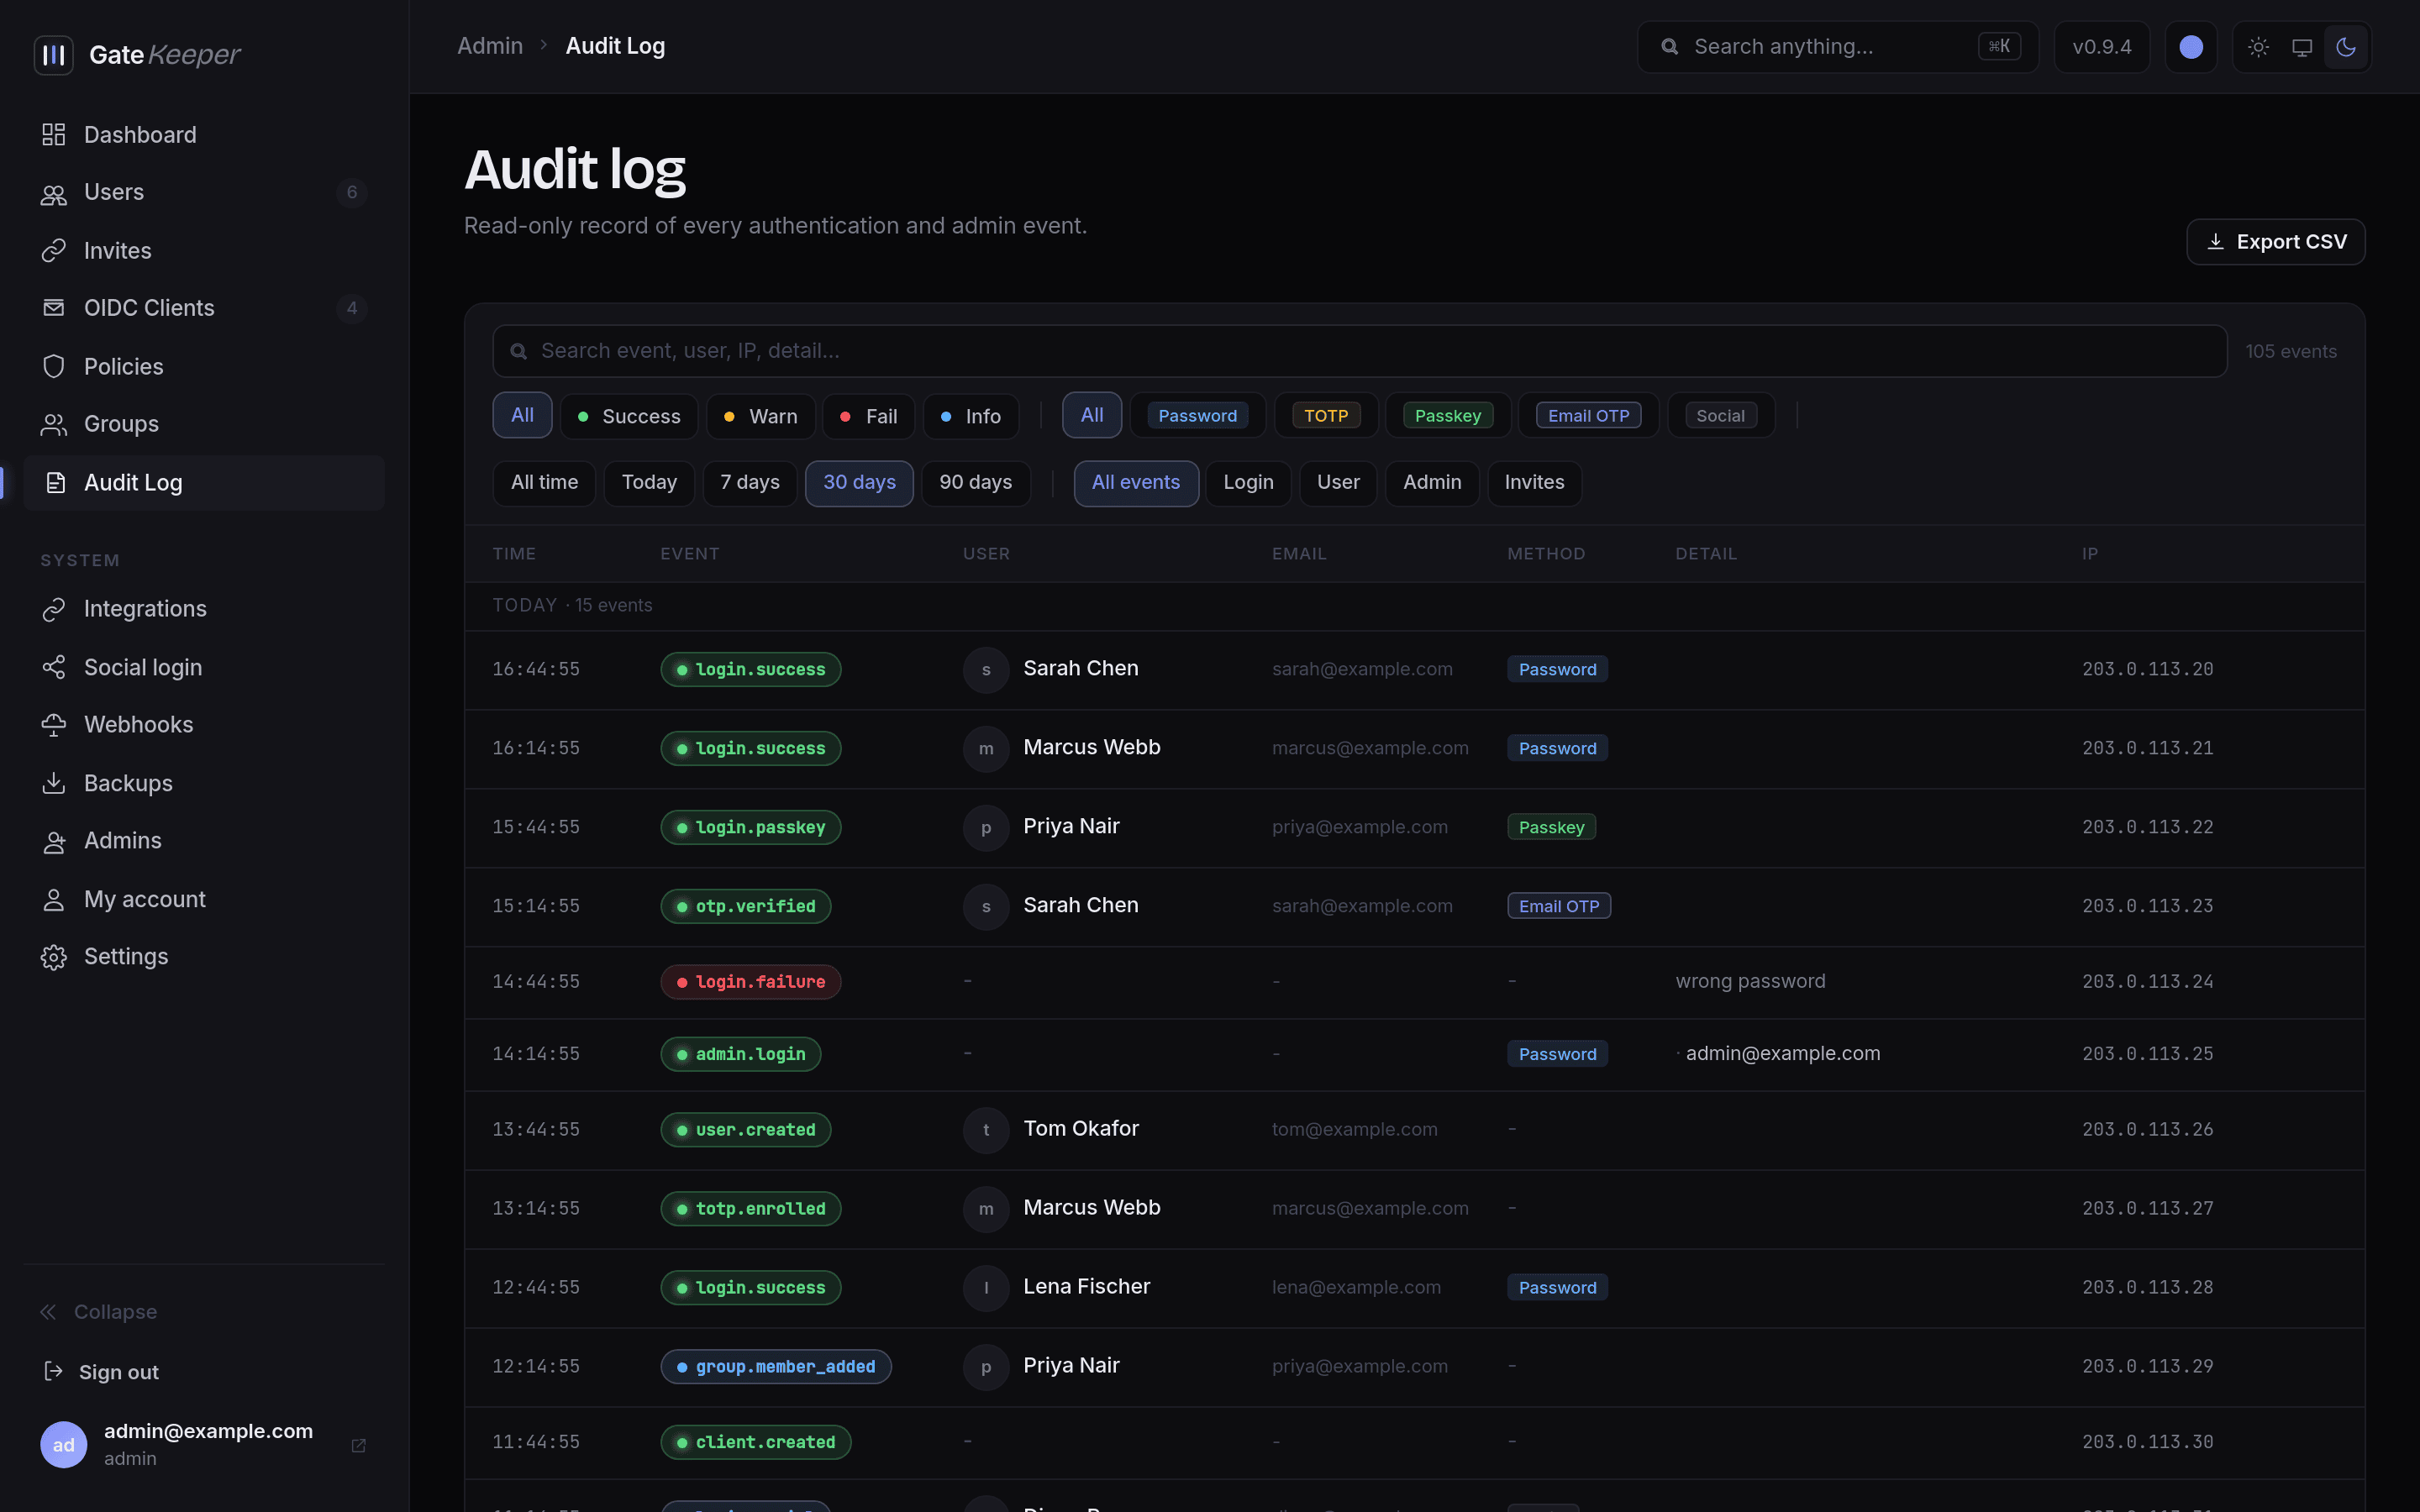
An append-only record of everything
Every authentication and admin event, filterable by category, outcome, sign-in method and date, and exportable as CSV. Failed sign-ins record why they failed and which address was tried.
Explore Audit log →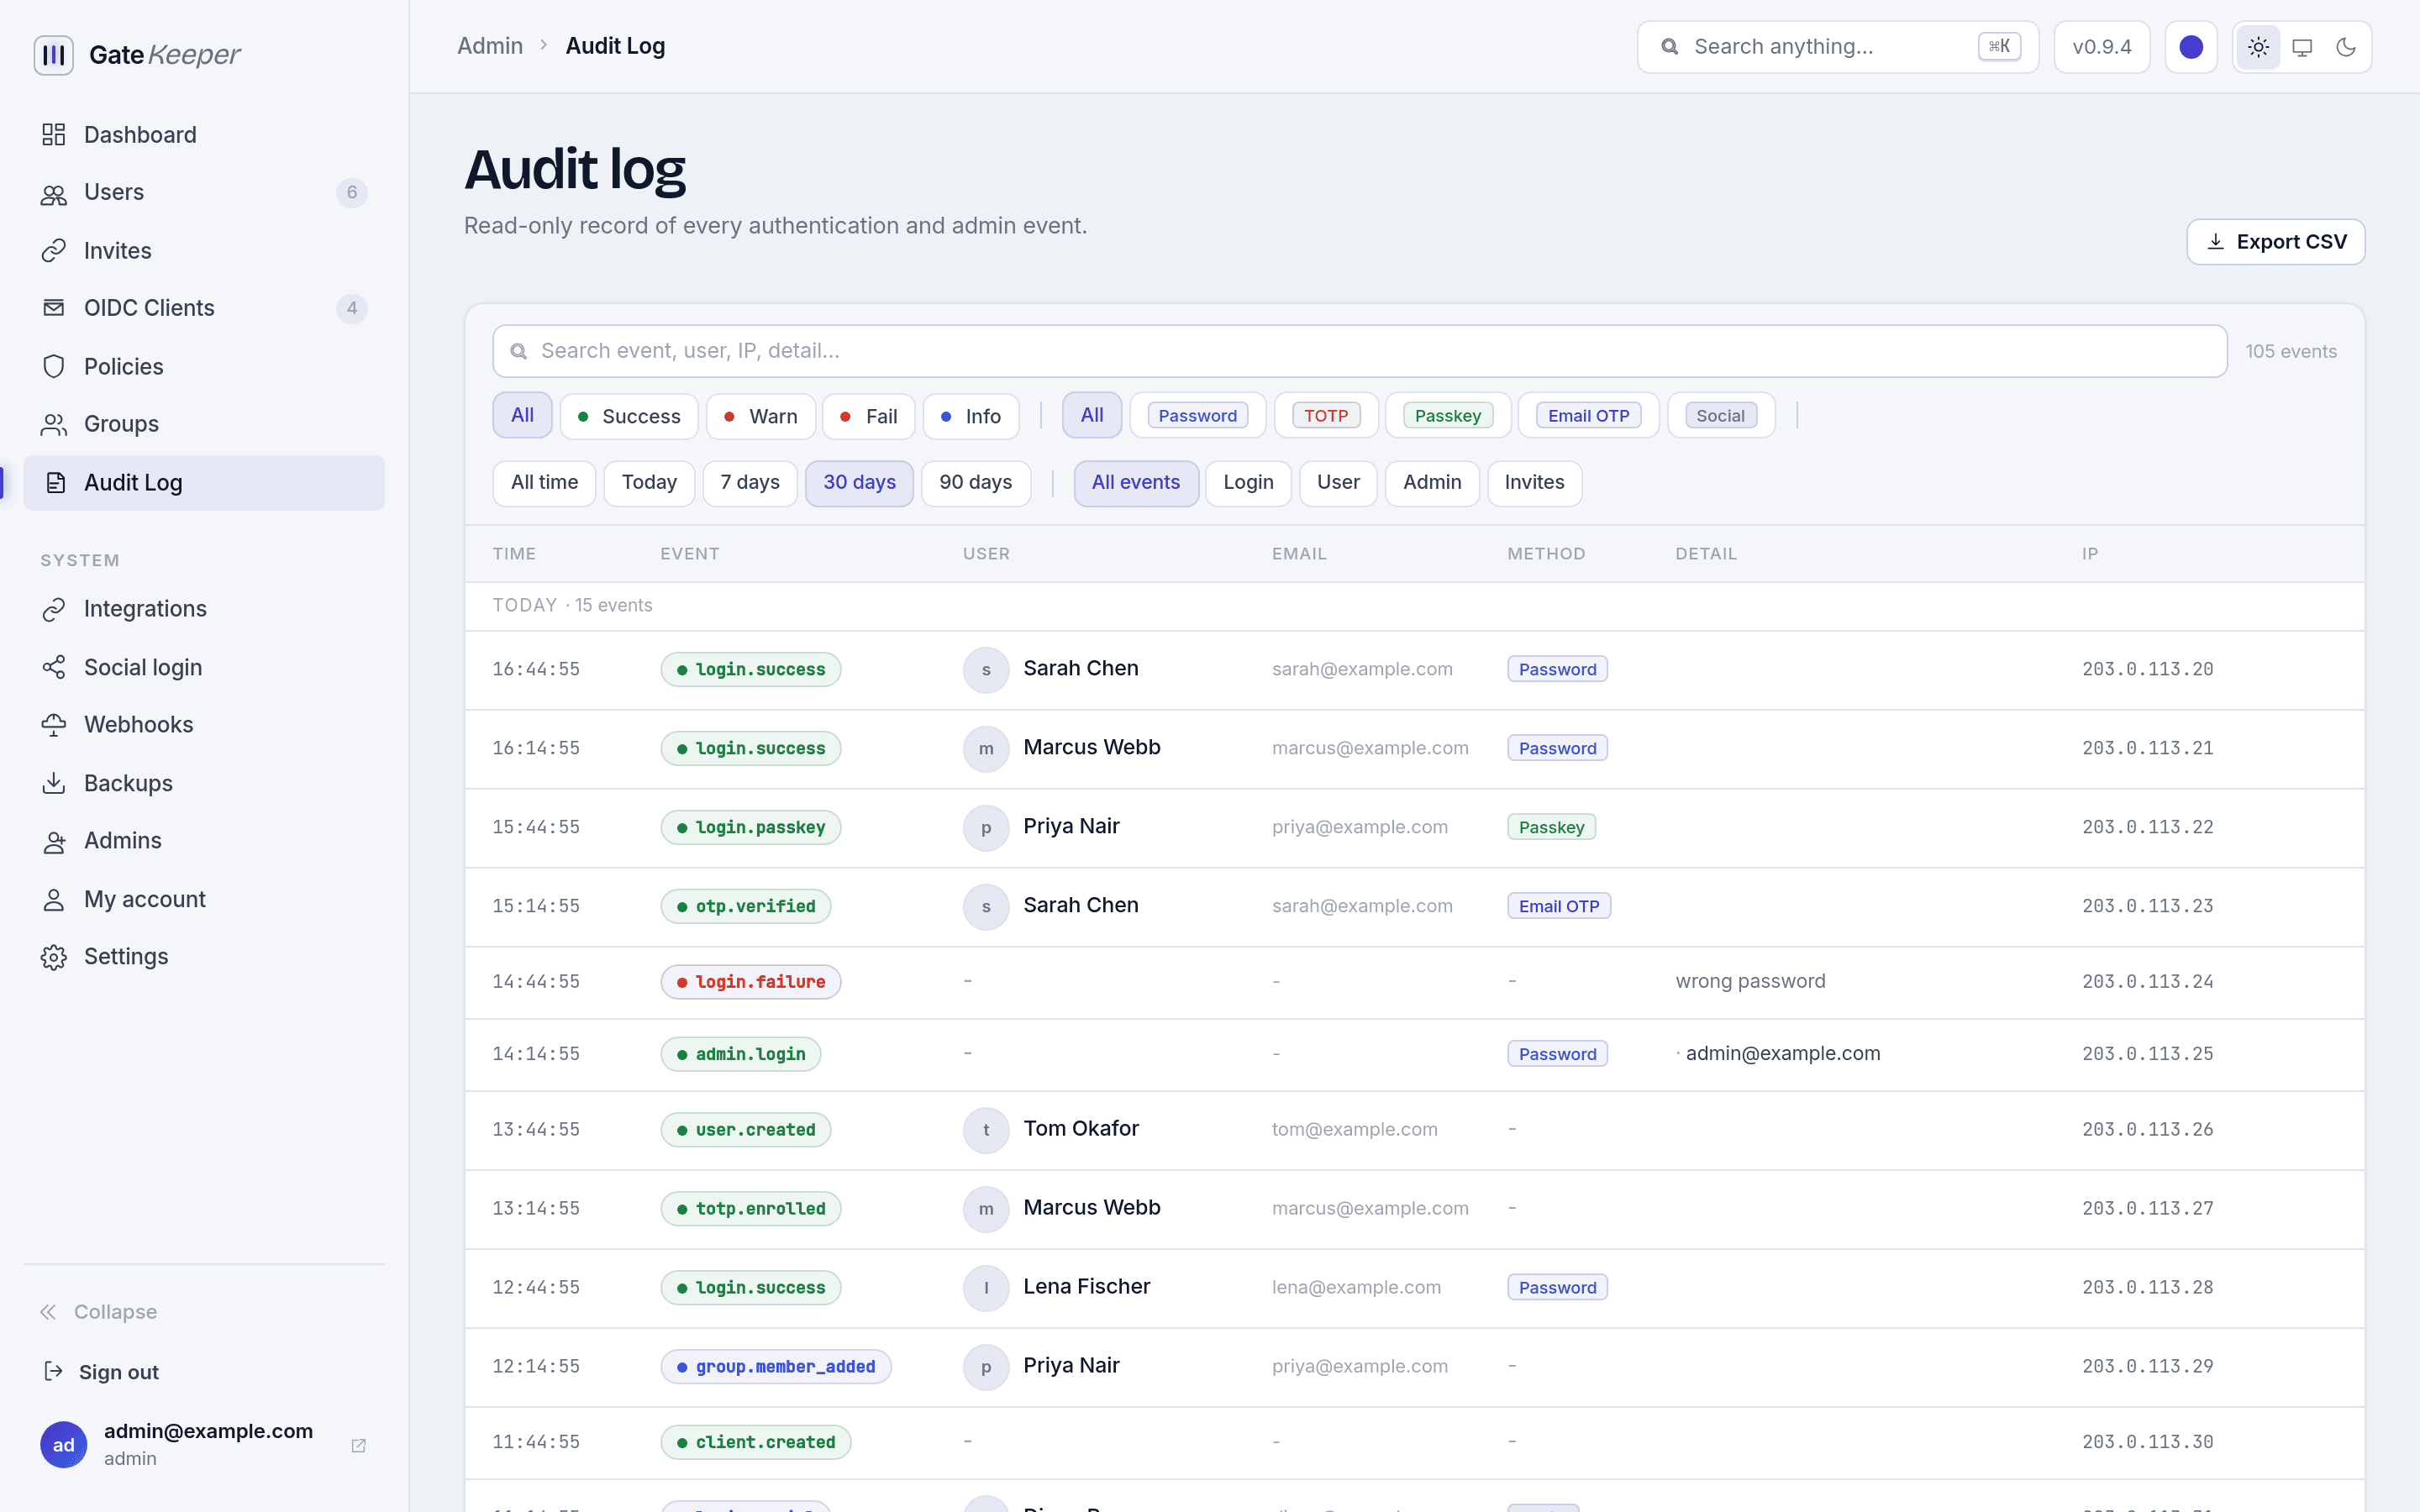
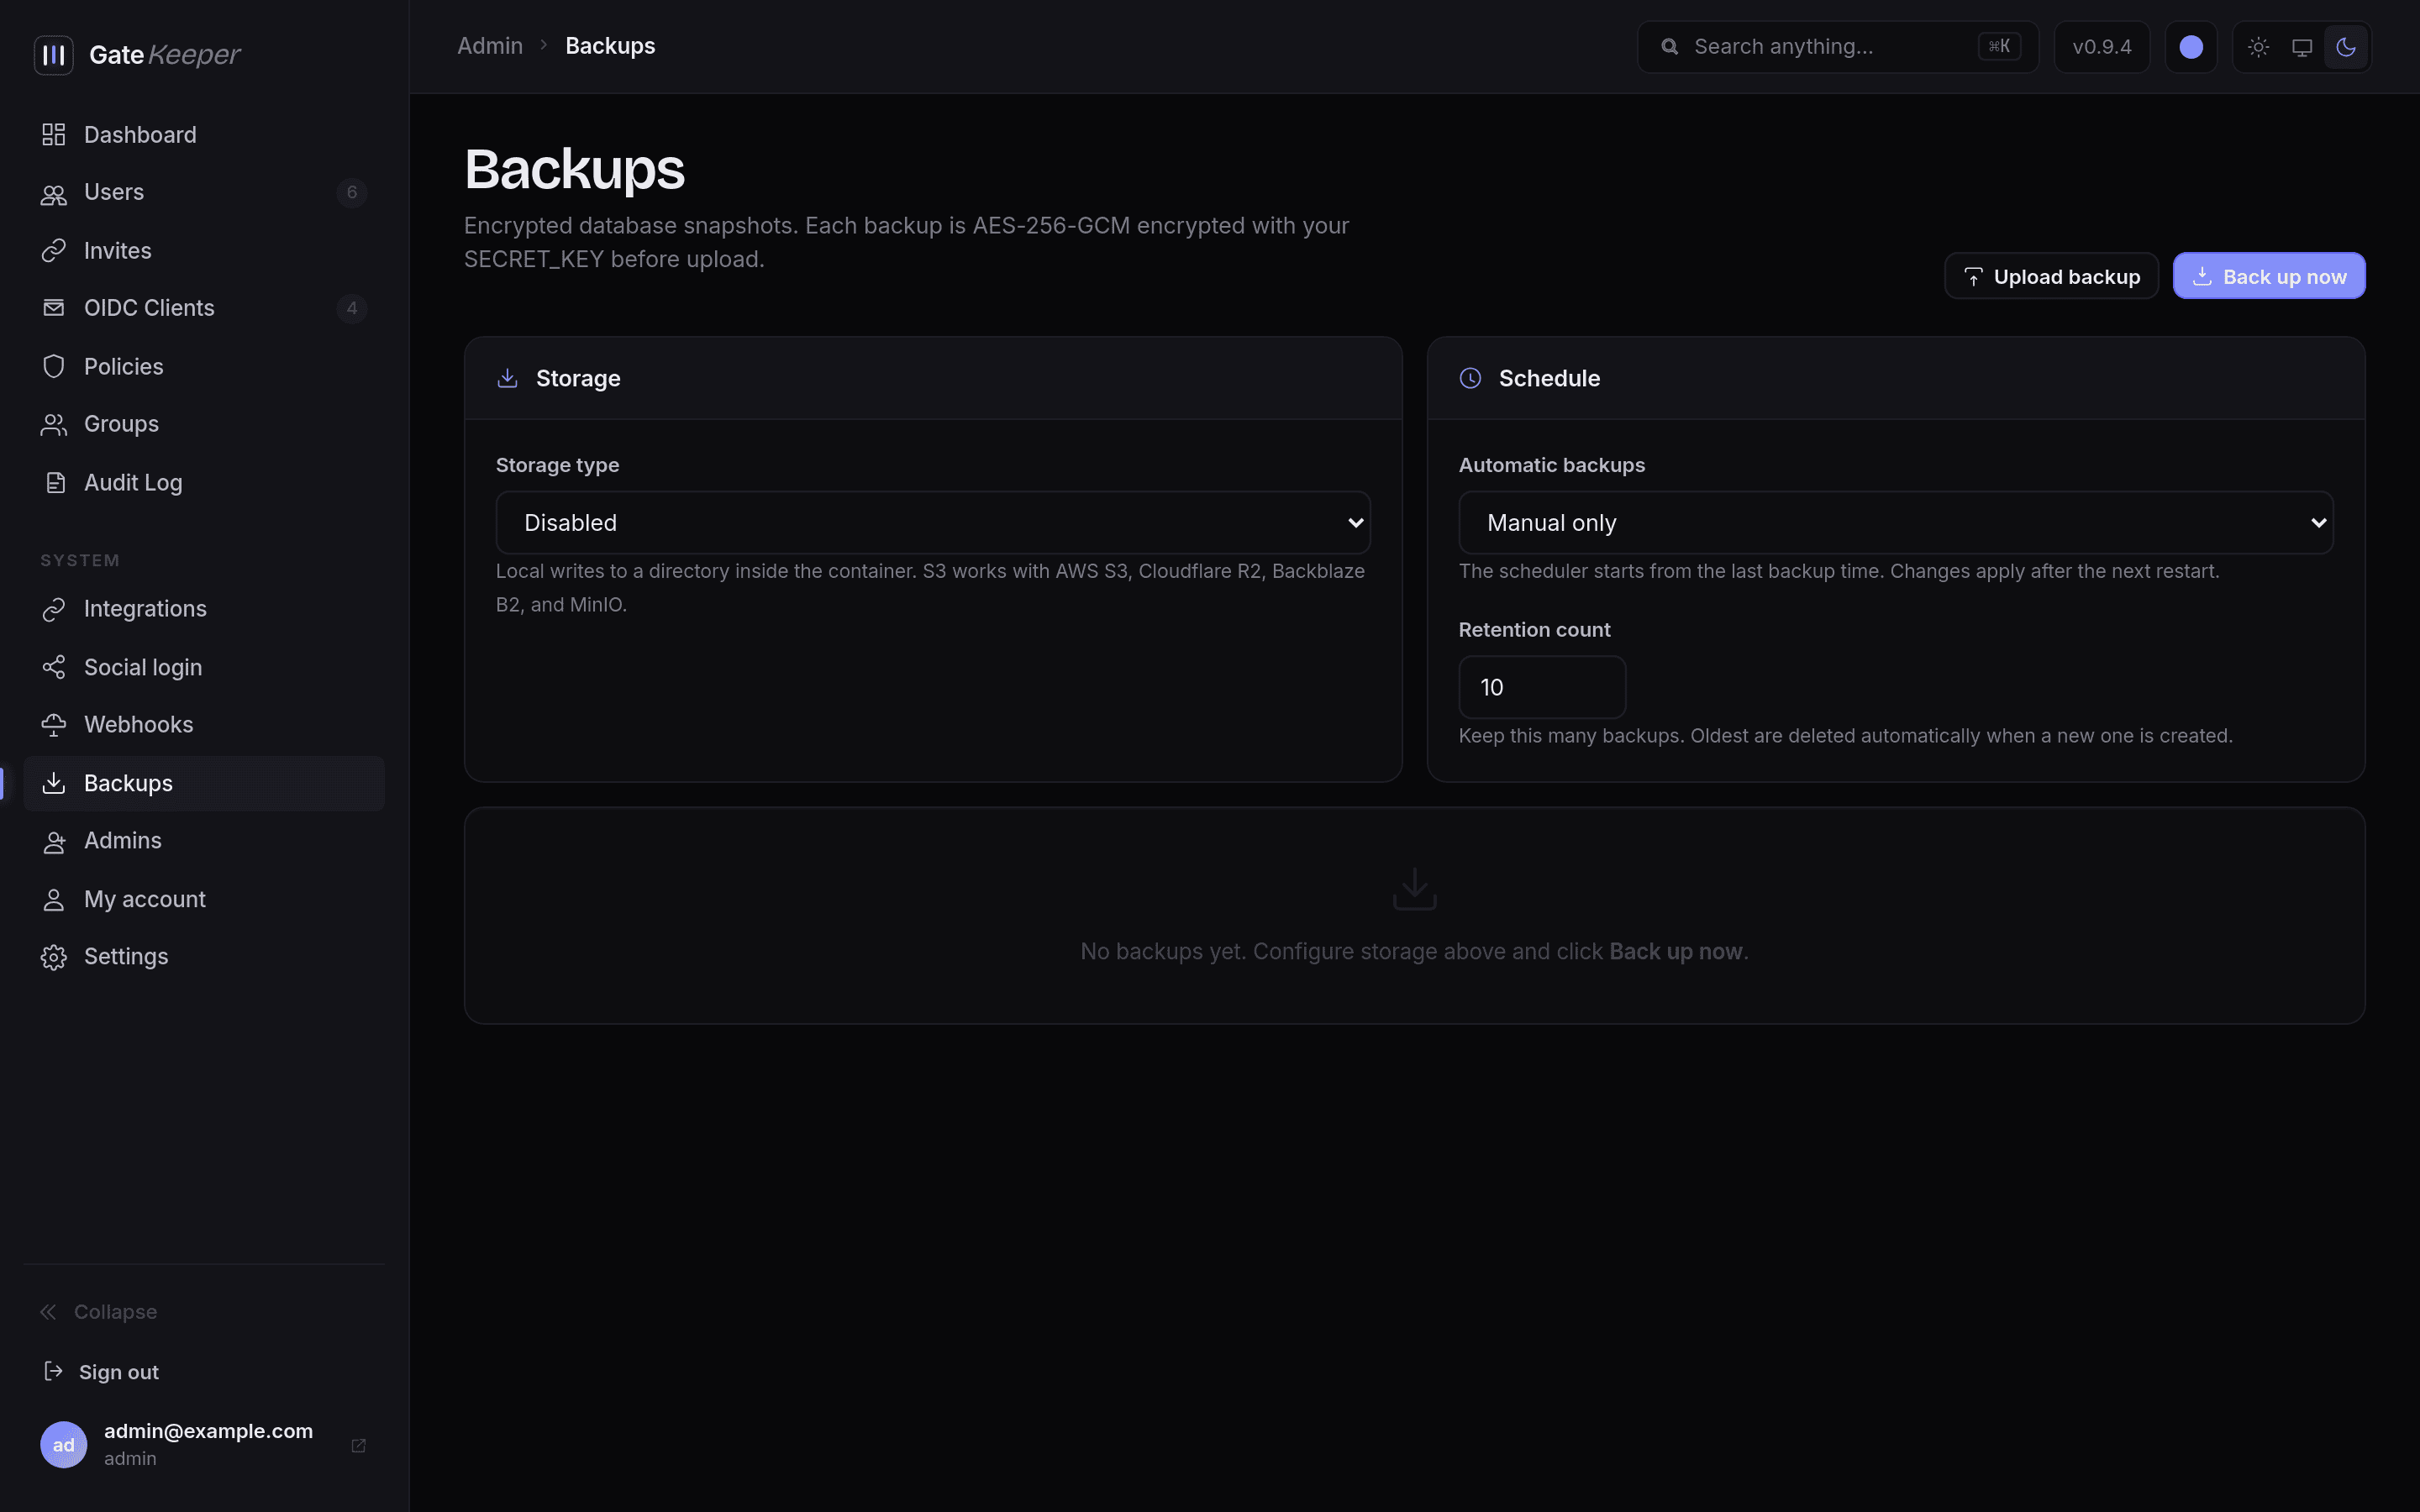
Encrypted snapshots, restored in a click
Scheduled or on-demand snapshots encrypted with AES-256-GCM, stored locally or in any S3-compatible bucket. Restoring stages the database and completes on the next restart.
Explore Backups →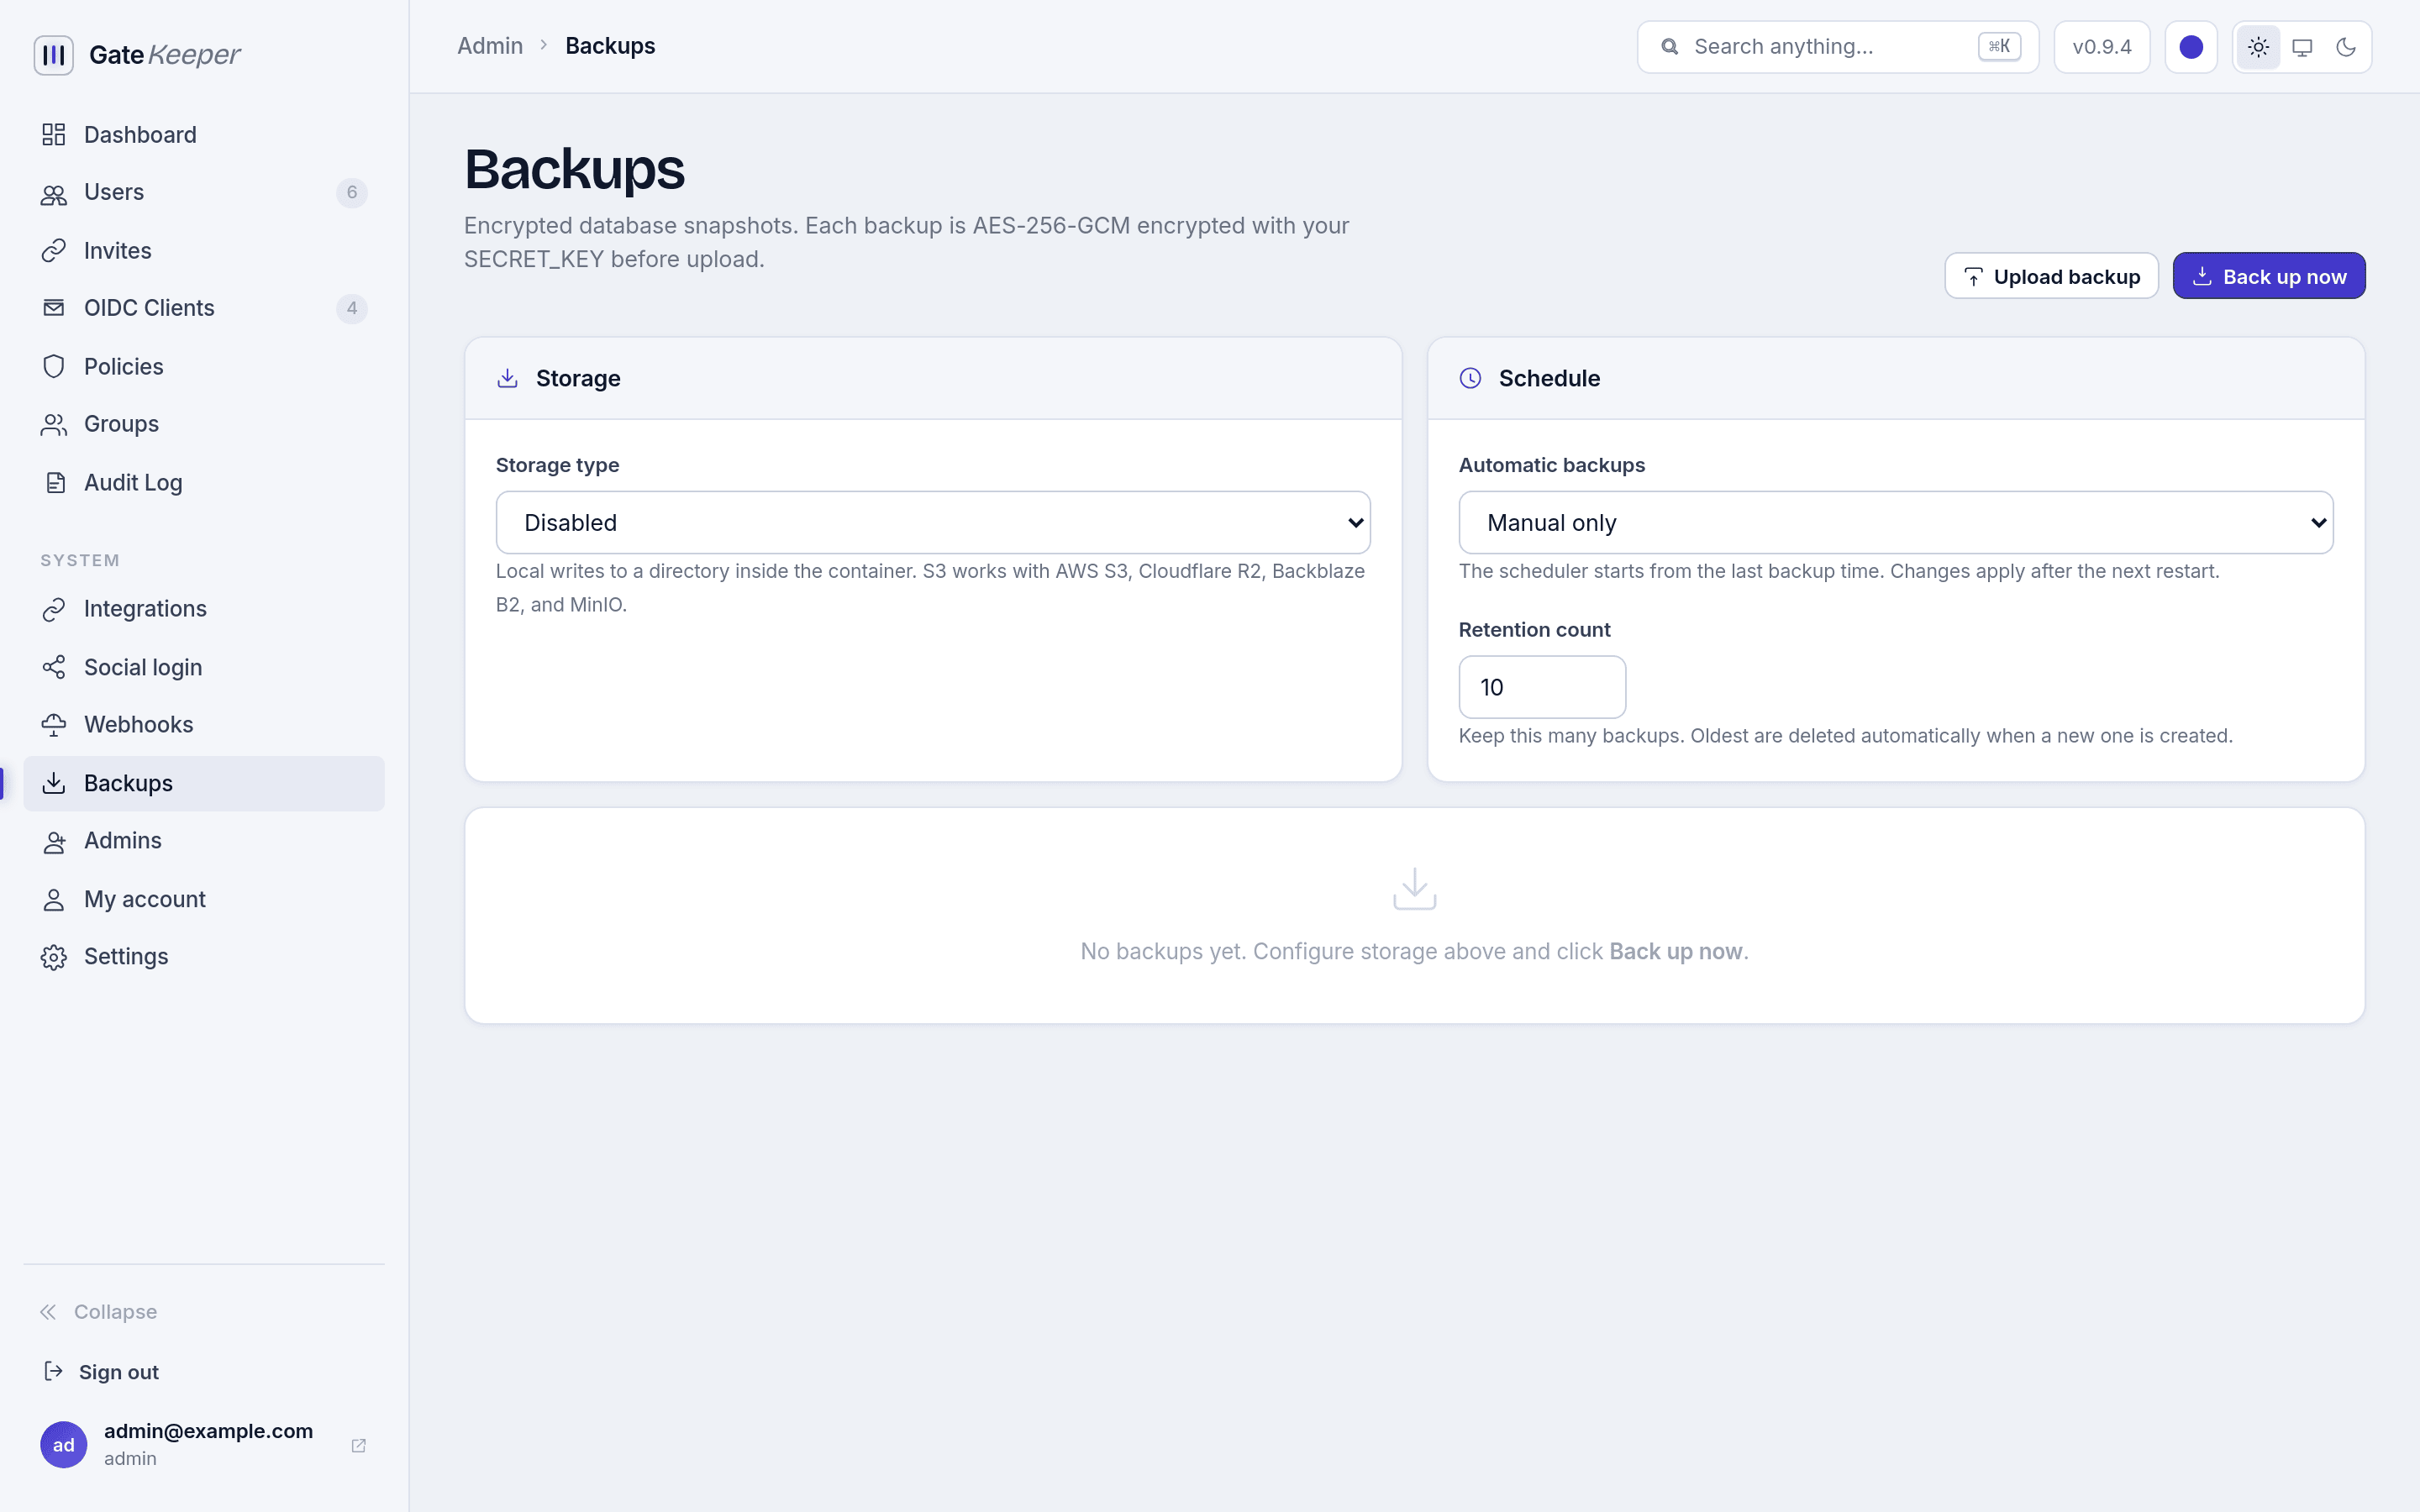
It keeps going
The whole thing fits in a pocket
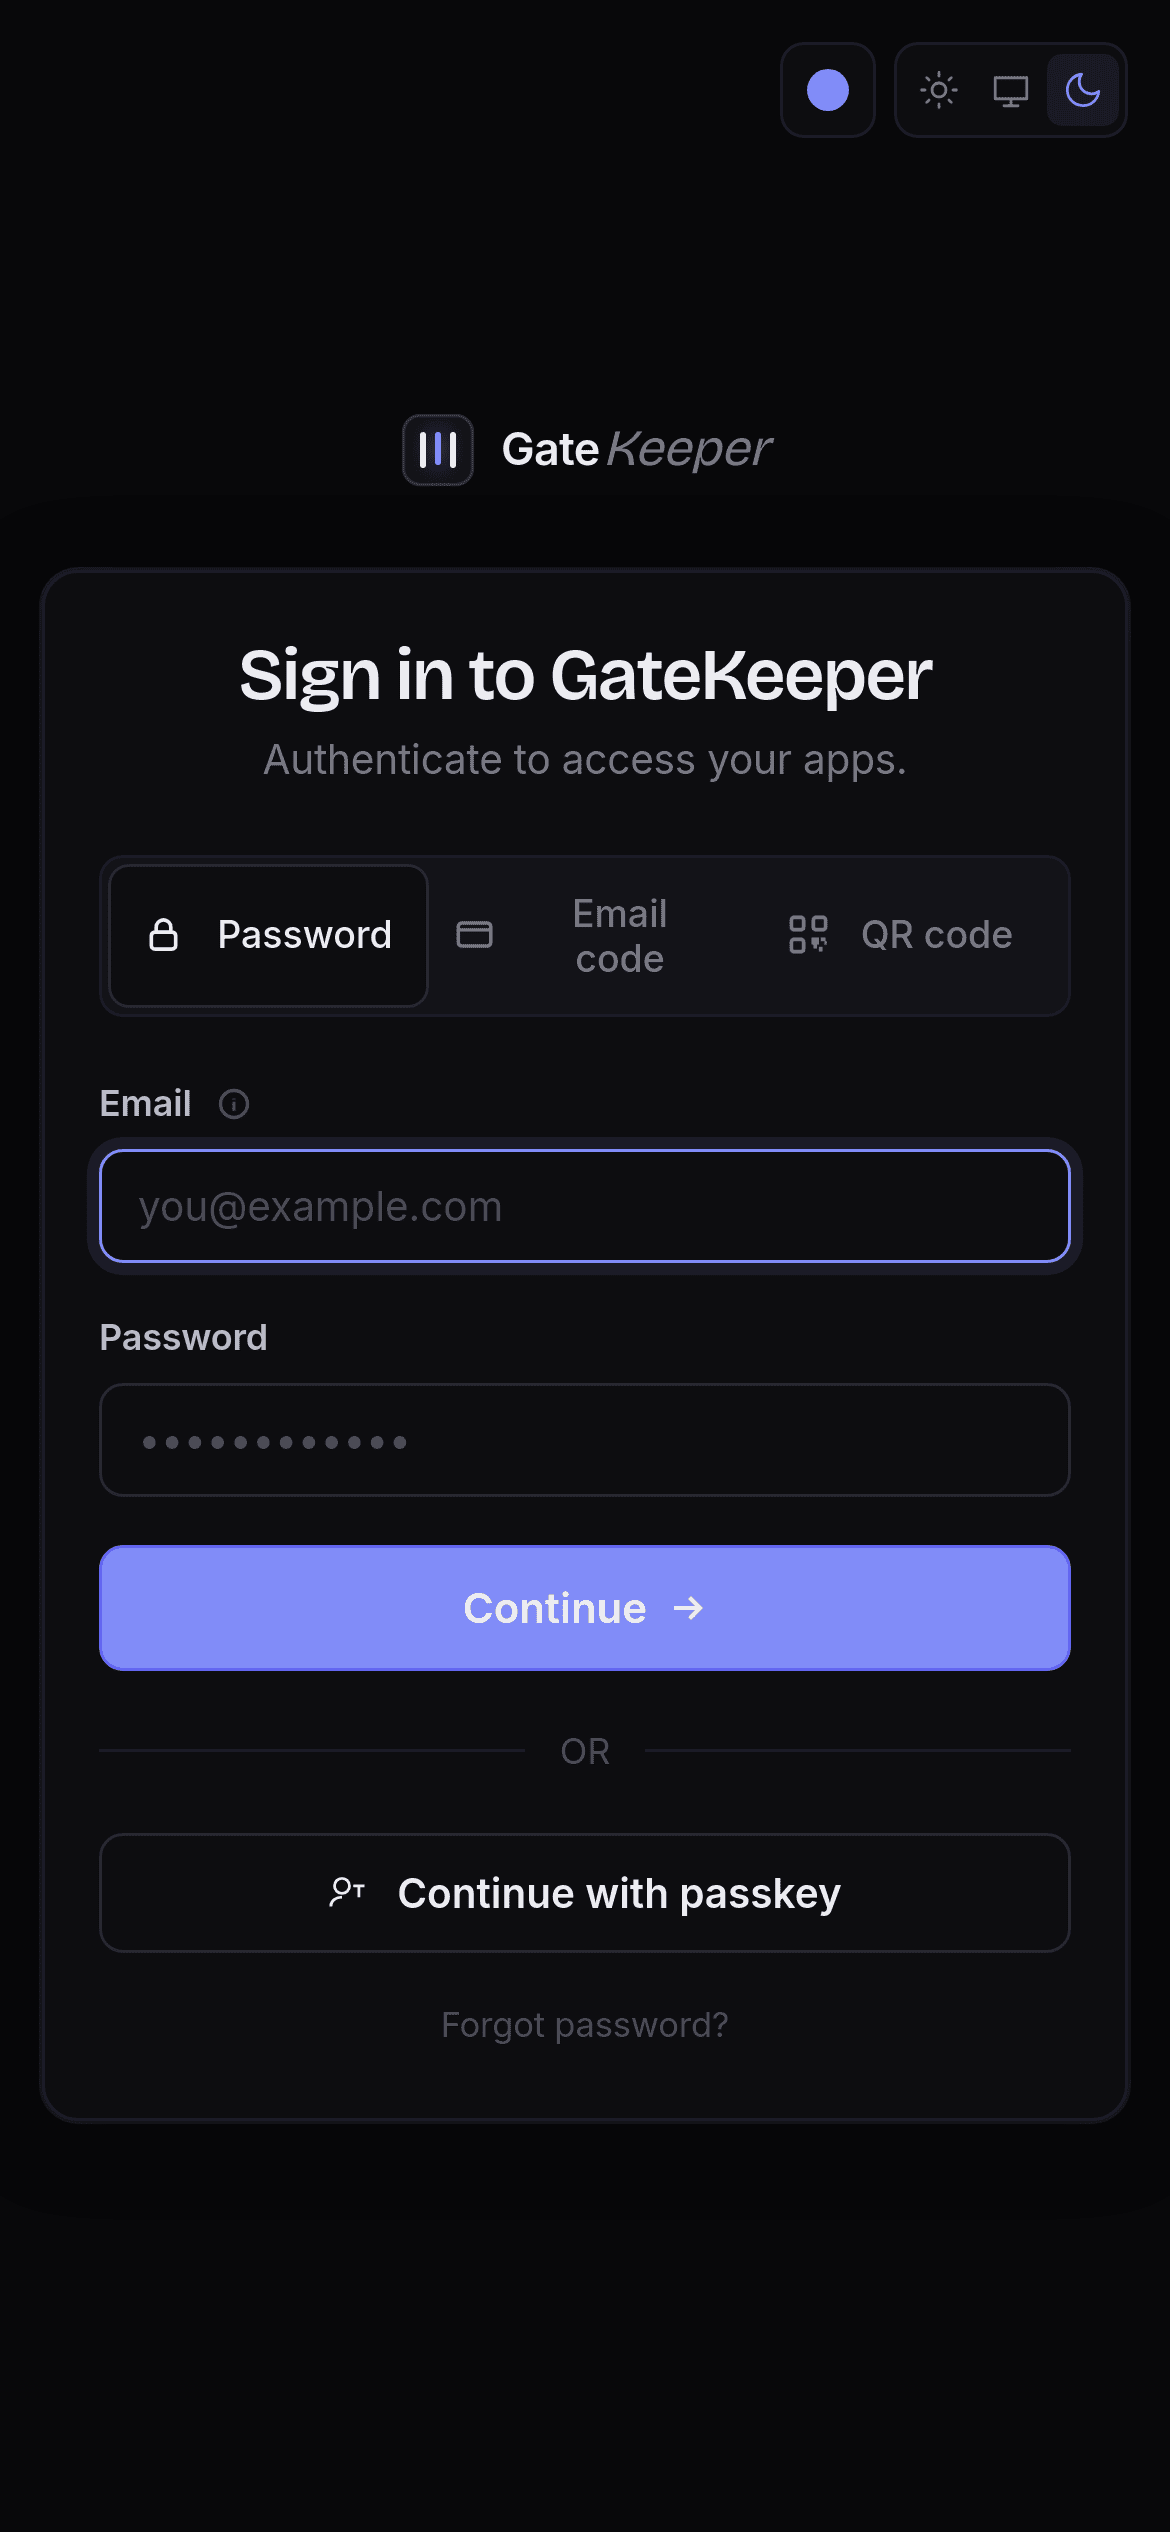
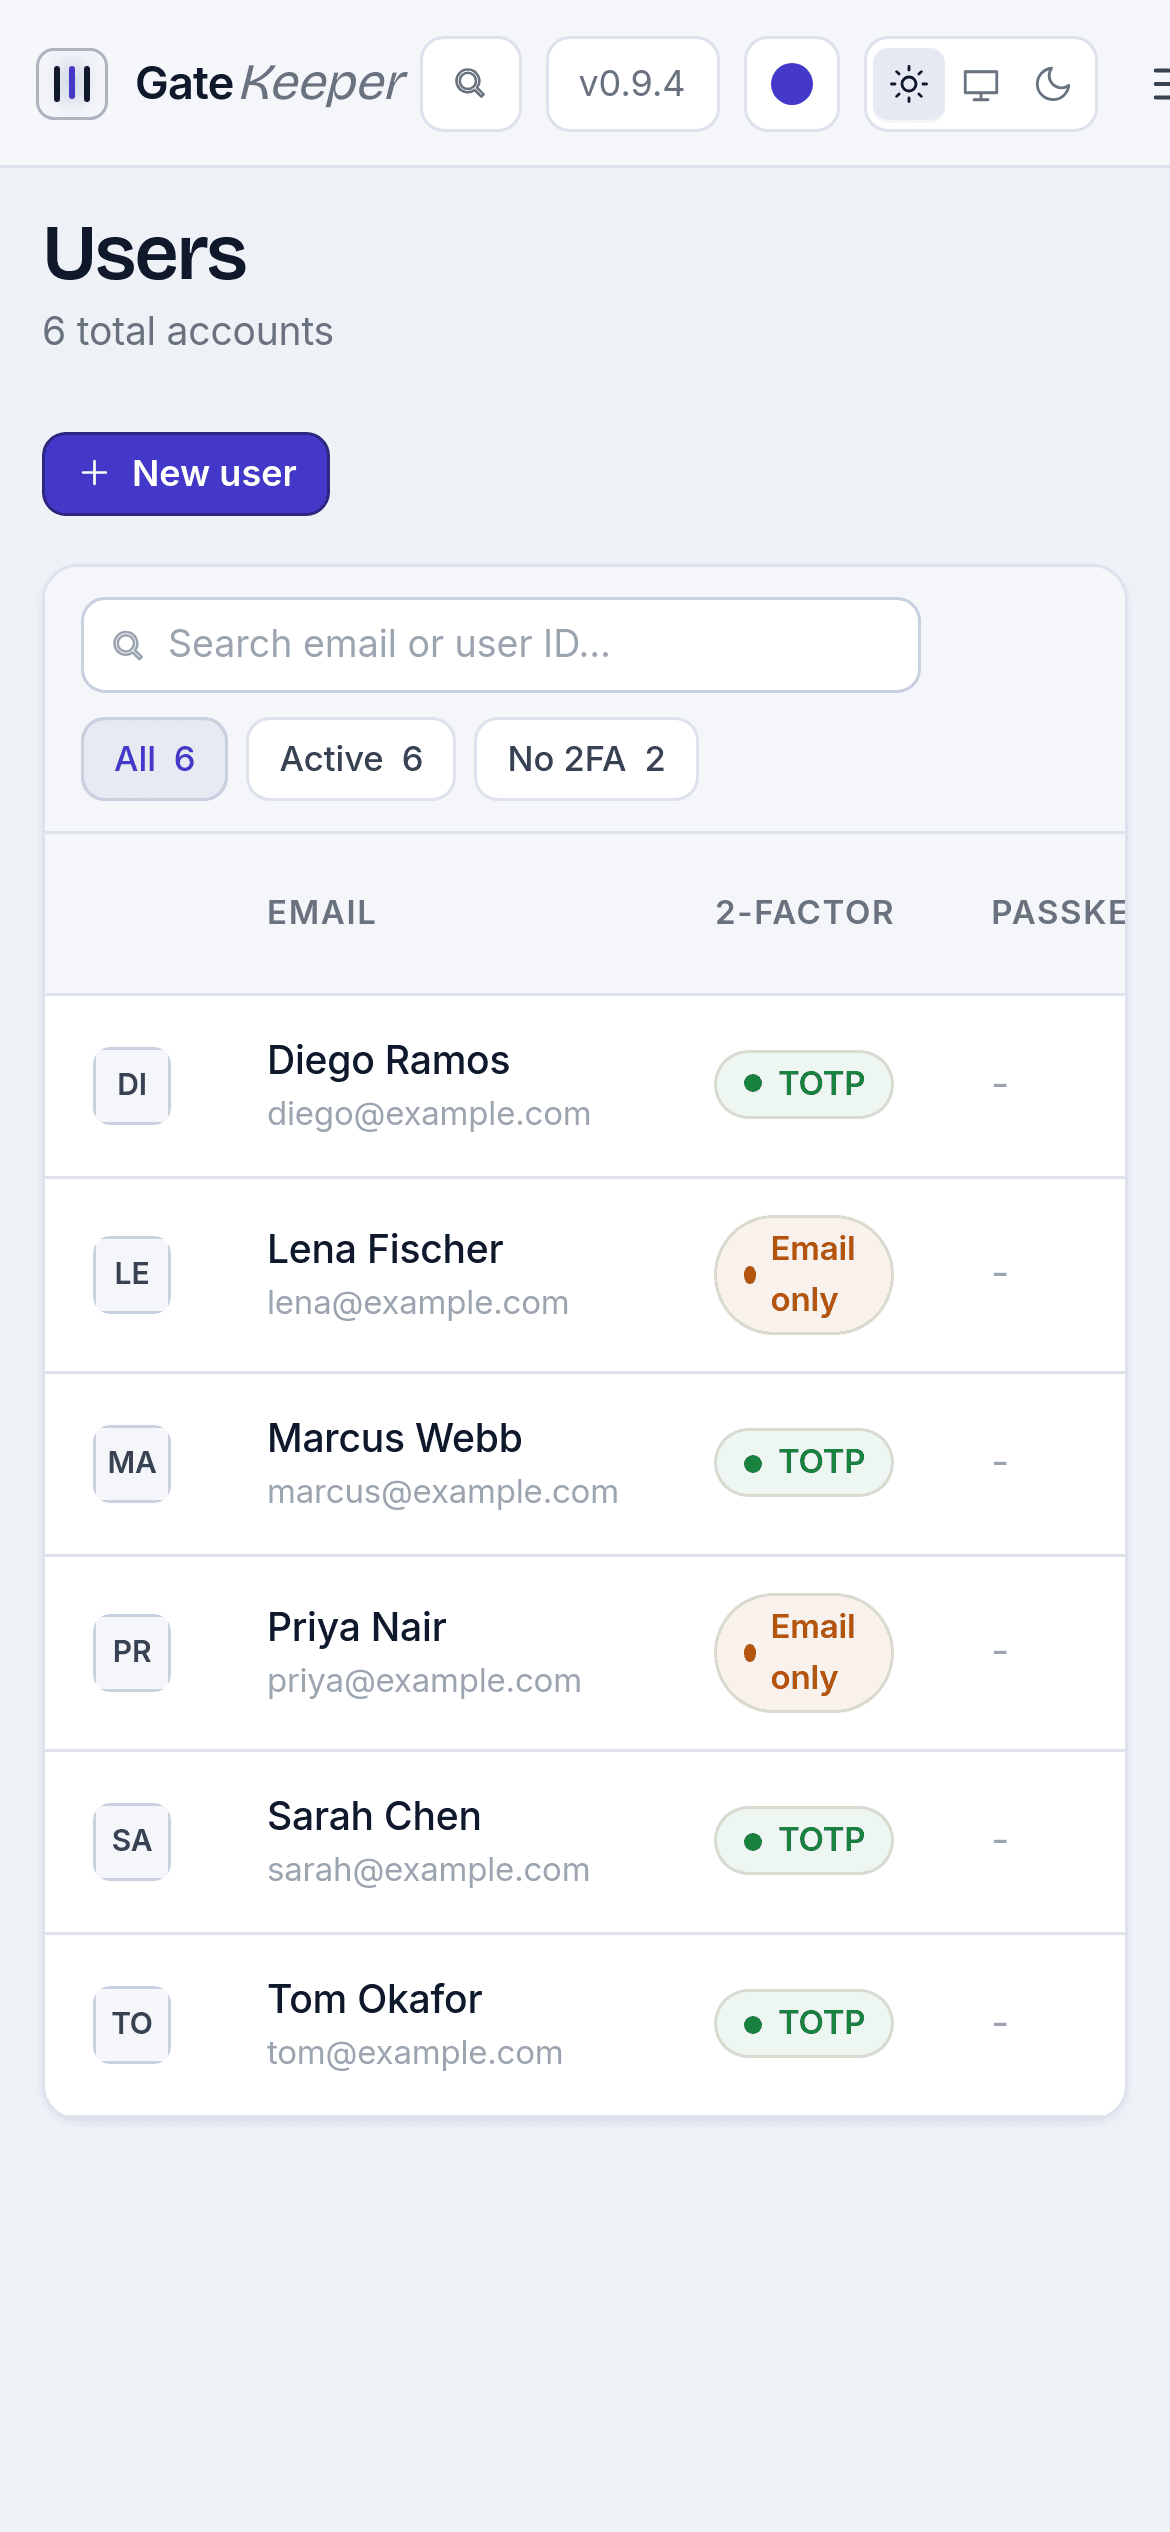
Every page adapts down to a phone, and both the user portal and the admin panel install to the home screen as their own app. Same light and dark themes.